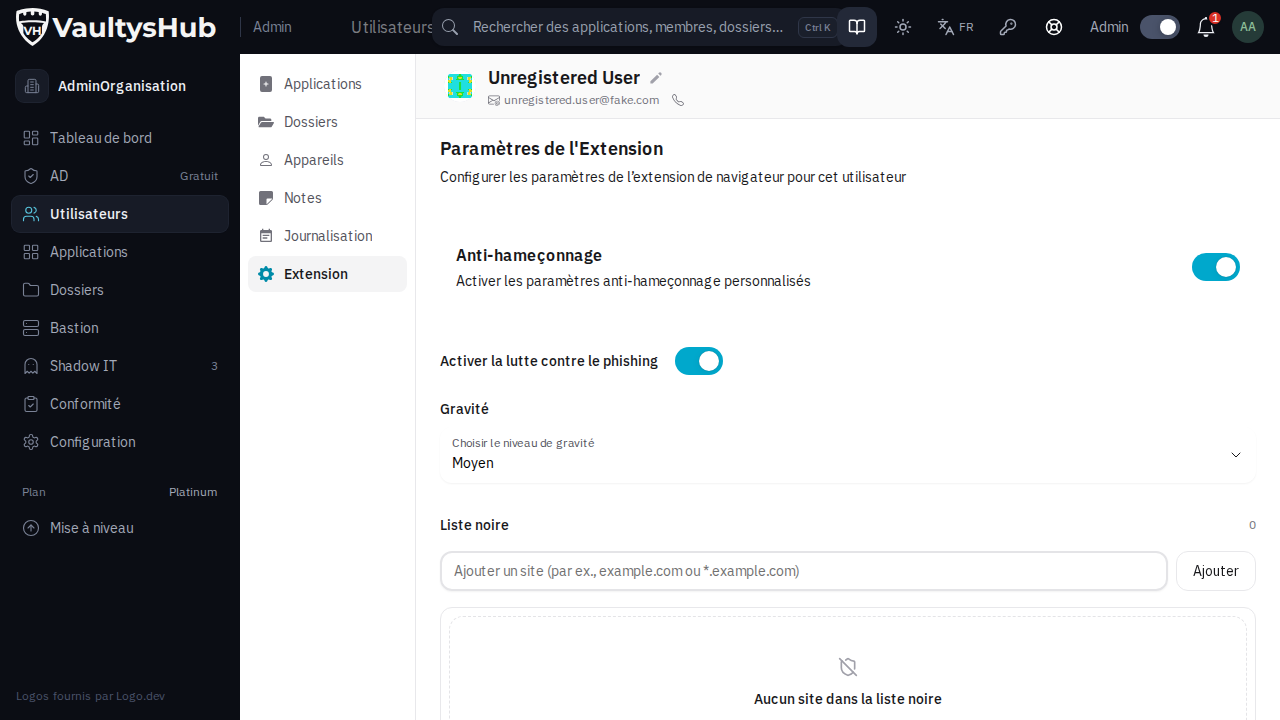
Anti-Phishing
The Anti-Phishing feature helps protect your users against phishing sites and phishing attempts while browsing with the VaultysHub extension. It can be configured both at the global organization level and individually for each user.
This feature is part of the Anti-phishing module. Without this module, the section appears locked, with a presentation of the module. See Pricing and Modules.
Global Configuration
Accessing Extension Settings
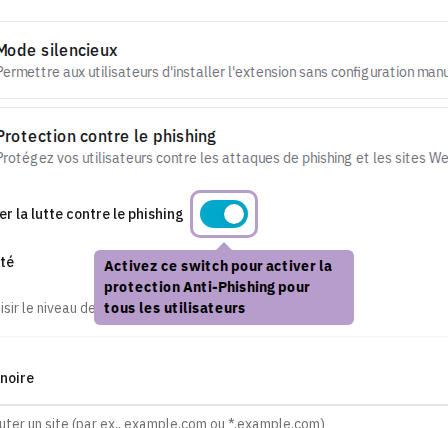
Go to Configuration → Extension tab.
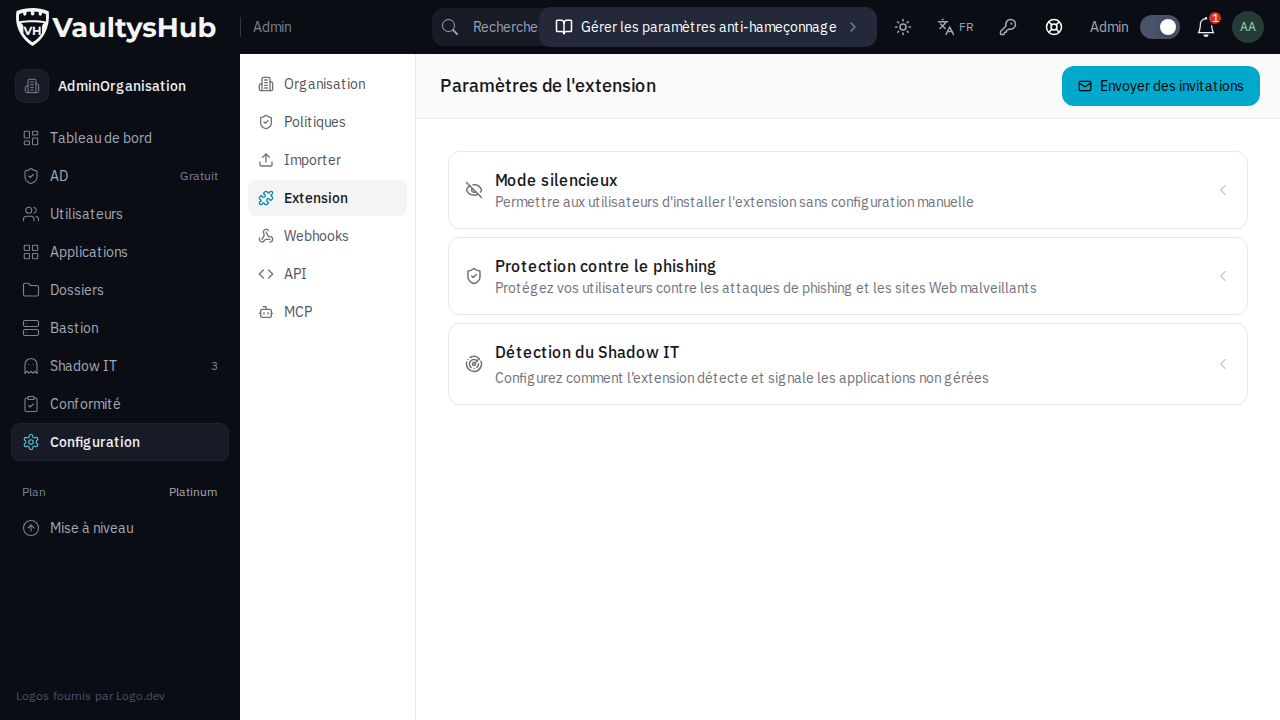
The page groups the features related to the VaultysHub browser extension. The Anti-Phishing Protection section is accessible via the dedicated menu.
Enable Anti-Phishing Protection
Click on the Anti-Phishing Protection section to expand it, then activate the switch Enable Phishing Protection.
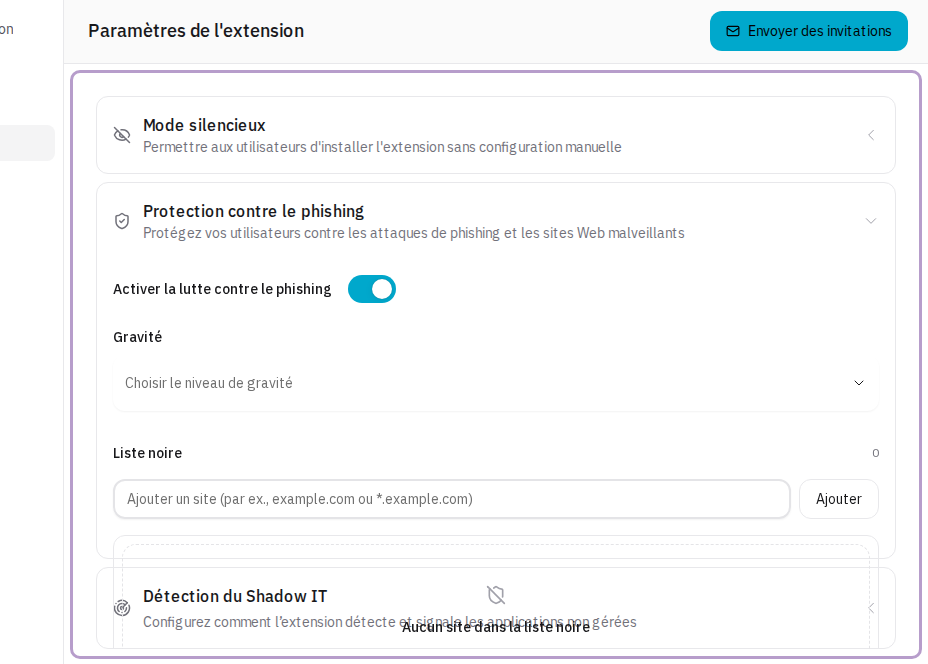
Choose the Severity Level
Once protection is activated, select the level of aggressiveness in the Severity menu.
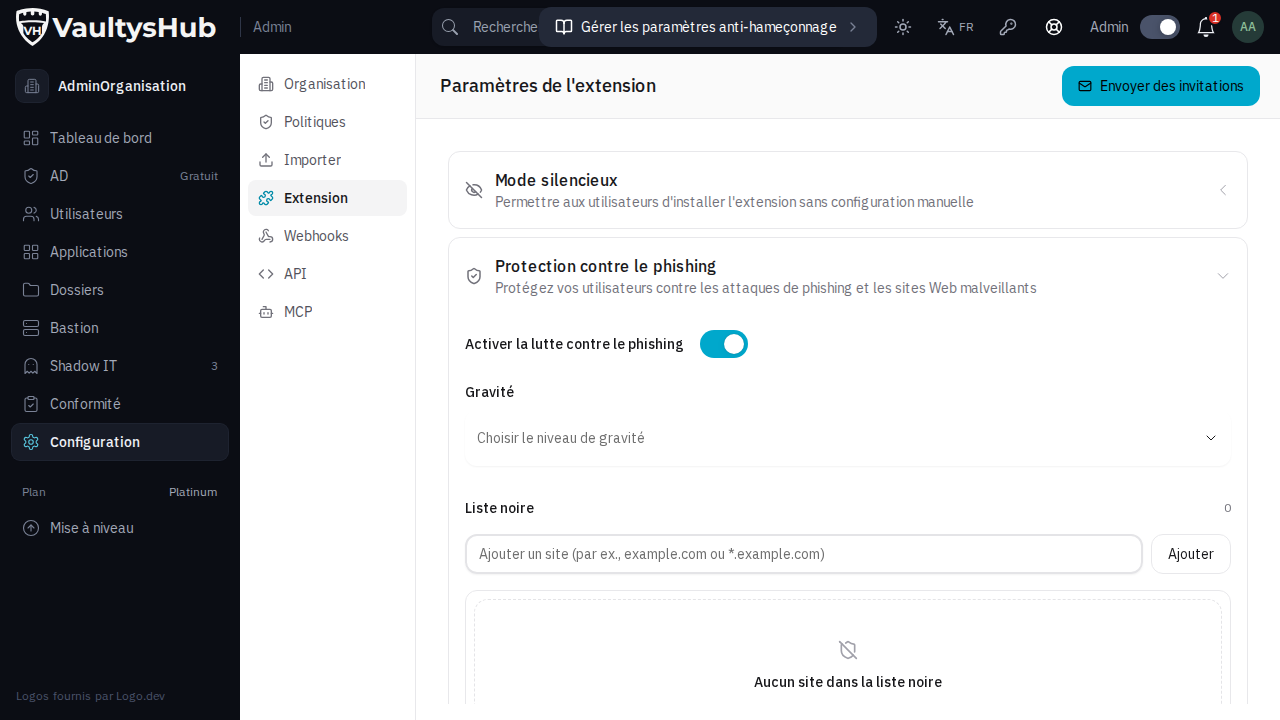
Two levels are available:
| Level | Behavior |
|---|---|
| Medium | Upon arriving at a login form on an unknown site, users see a warning appear over the form. They can easily dismiss it and continue. |
| High | The warning is permanent: users cannot dismiss it and therefore cannot log in to the unknown site. |
Manage the Domain Blacklist
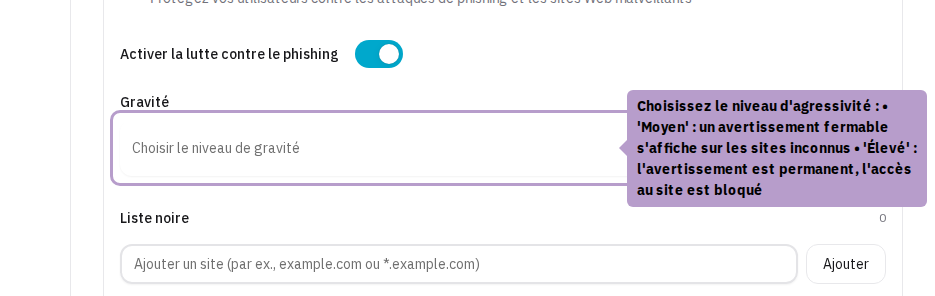
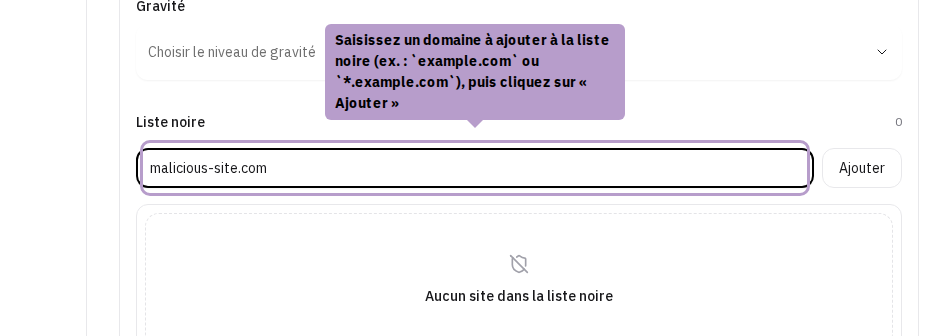
The Blacklist allows explicitly referencing domains to block, regardless of the configured severity.
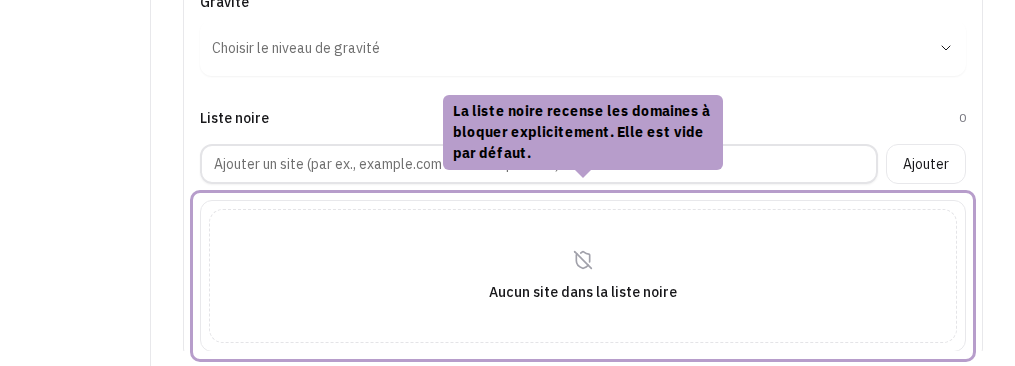
Enter a domain in the input field (e.g., malicious-site.com or *.malicious-site.com) and then click Add to include it.
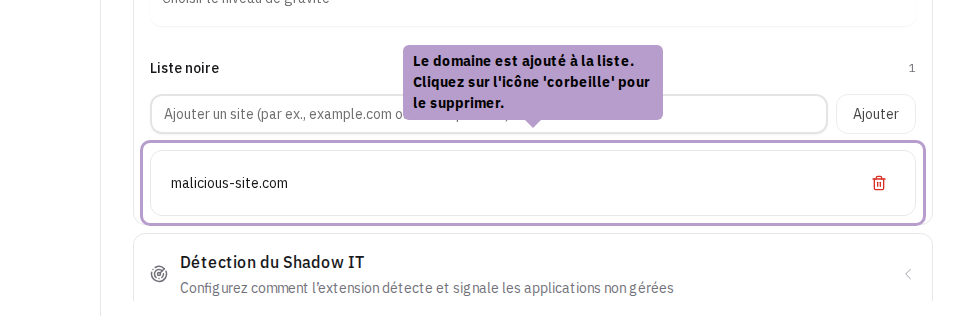
Click on the trash icon to the right of a domain to remove it from the blacklist.
User-Specific Configuration
It is possible to define specific Anti-Phishing settings for a user, independently of the global organization configuration.
Accessing a User's Profile
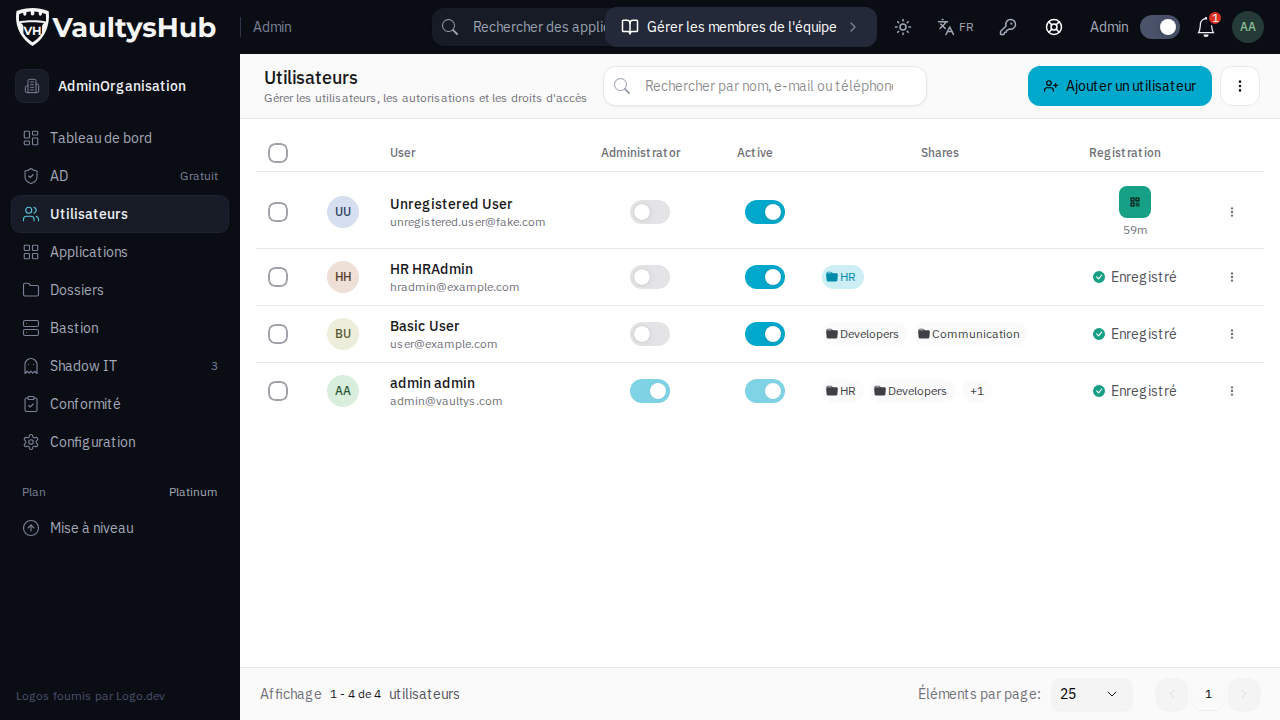
Go to Users from the navigation bar, then click on the action menu of a user and select Profile.
Extension Settings Tab
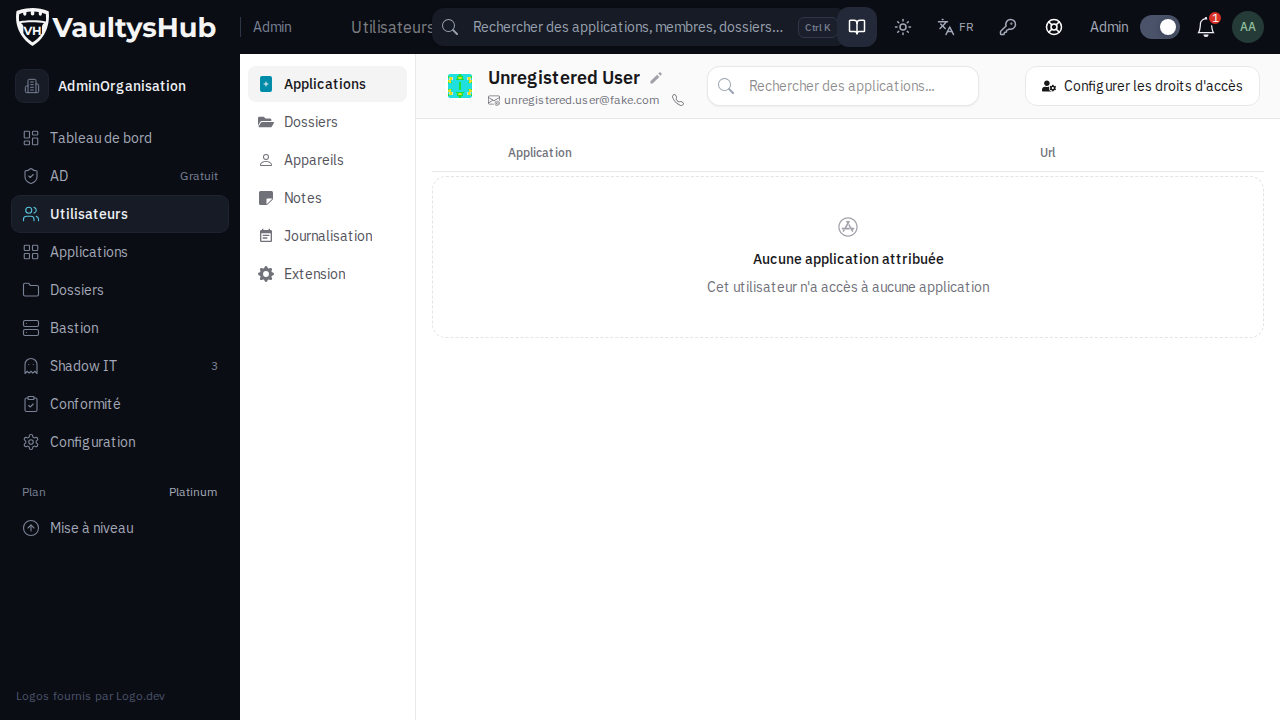
In the user's profile, click on the Extension tab.
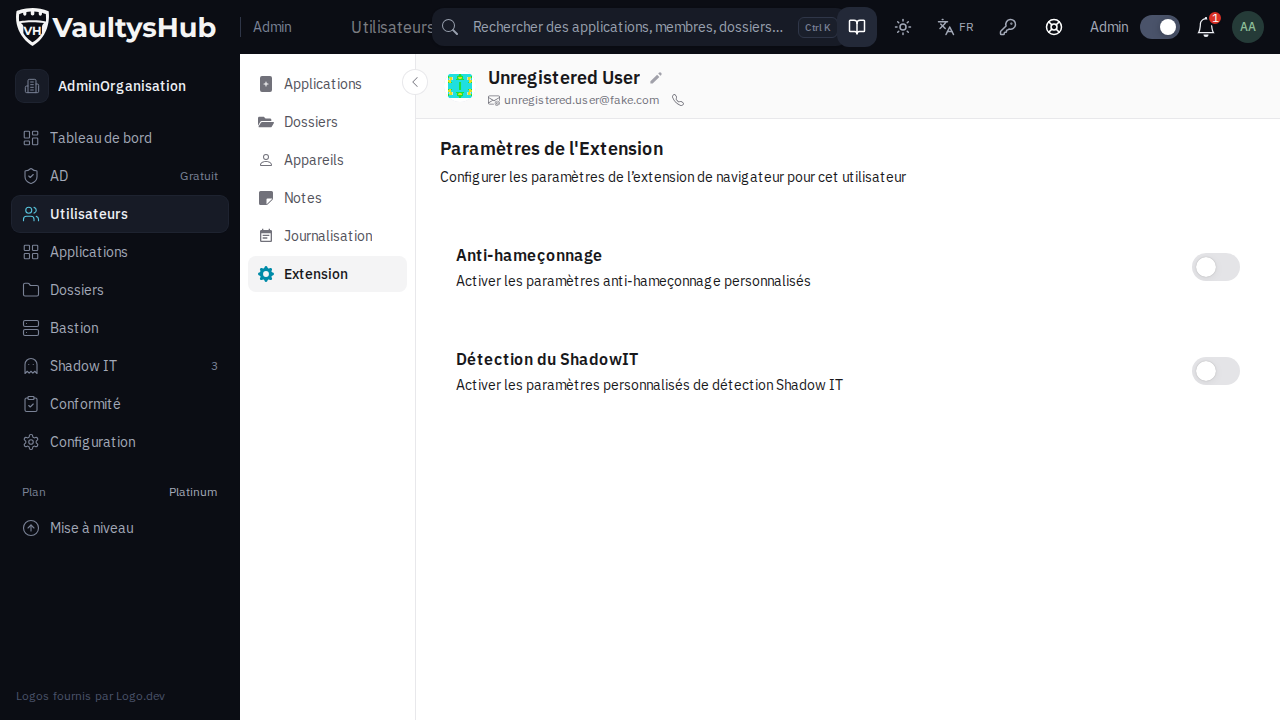
The Anti-Phishing section displays a switch allowing you to activate settings specific to this user.
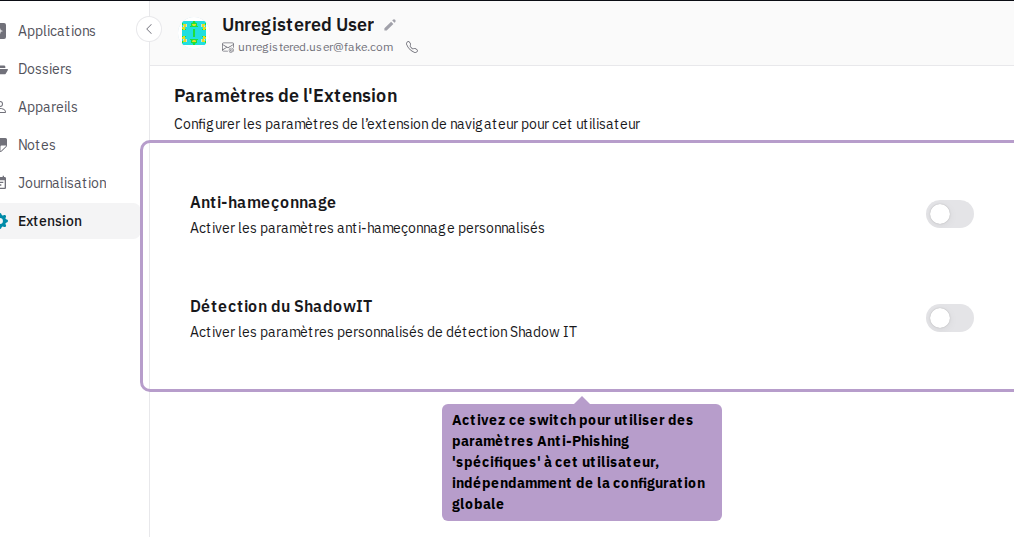
Enable the switch Activate Custom Anti-Phishing Settings to override the global configuration with settings specific to this user. The configuration is then done in the same way as for global settings: activation, severity level, and domain blacklist.