Access Rules
The Access Rules (Device Access Policies) allow the administrator to finely control the conditions under which users can authenticate: browser type, operating system, security level of the VaultysID identity, allowed IP addresses, etc.
Three policy scopes are available:
- Global — applies to all users in the organization.
- Admin — applies only to administrators.
- Group — applies to a defined set of users and/or folders.
Access rules are part of the Bastion module. Without this module, the tab appears locked, with a presentation of the module. See Pricing and Modules.
Overview
Access the access rules from the Configuration menu, Policies tab.
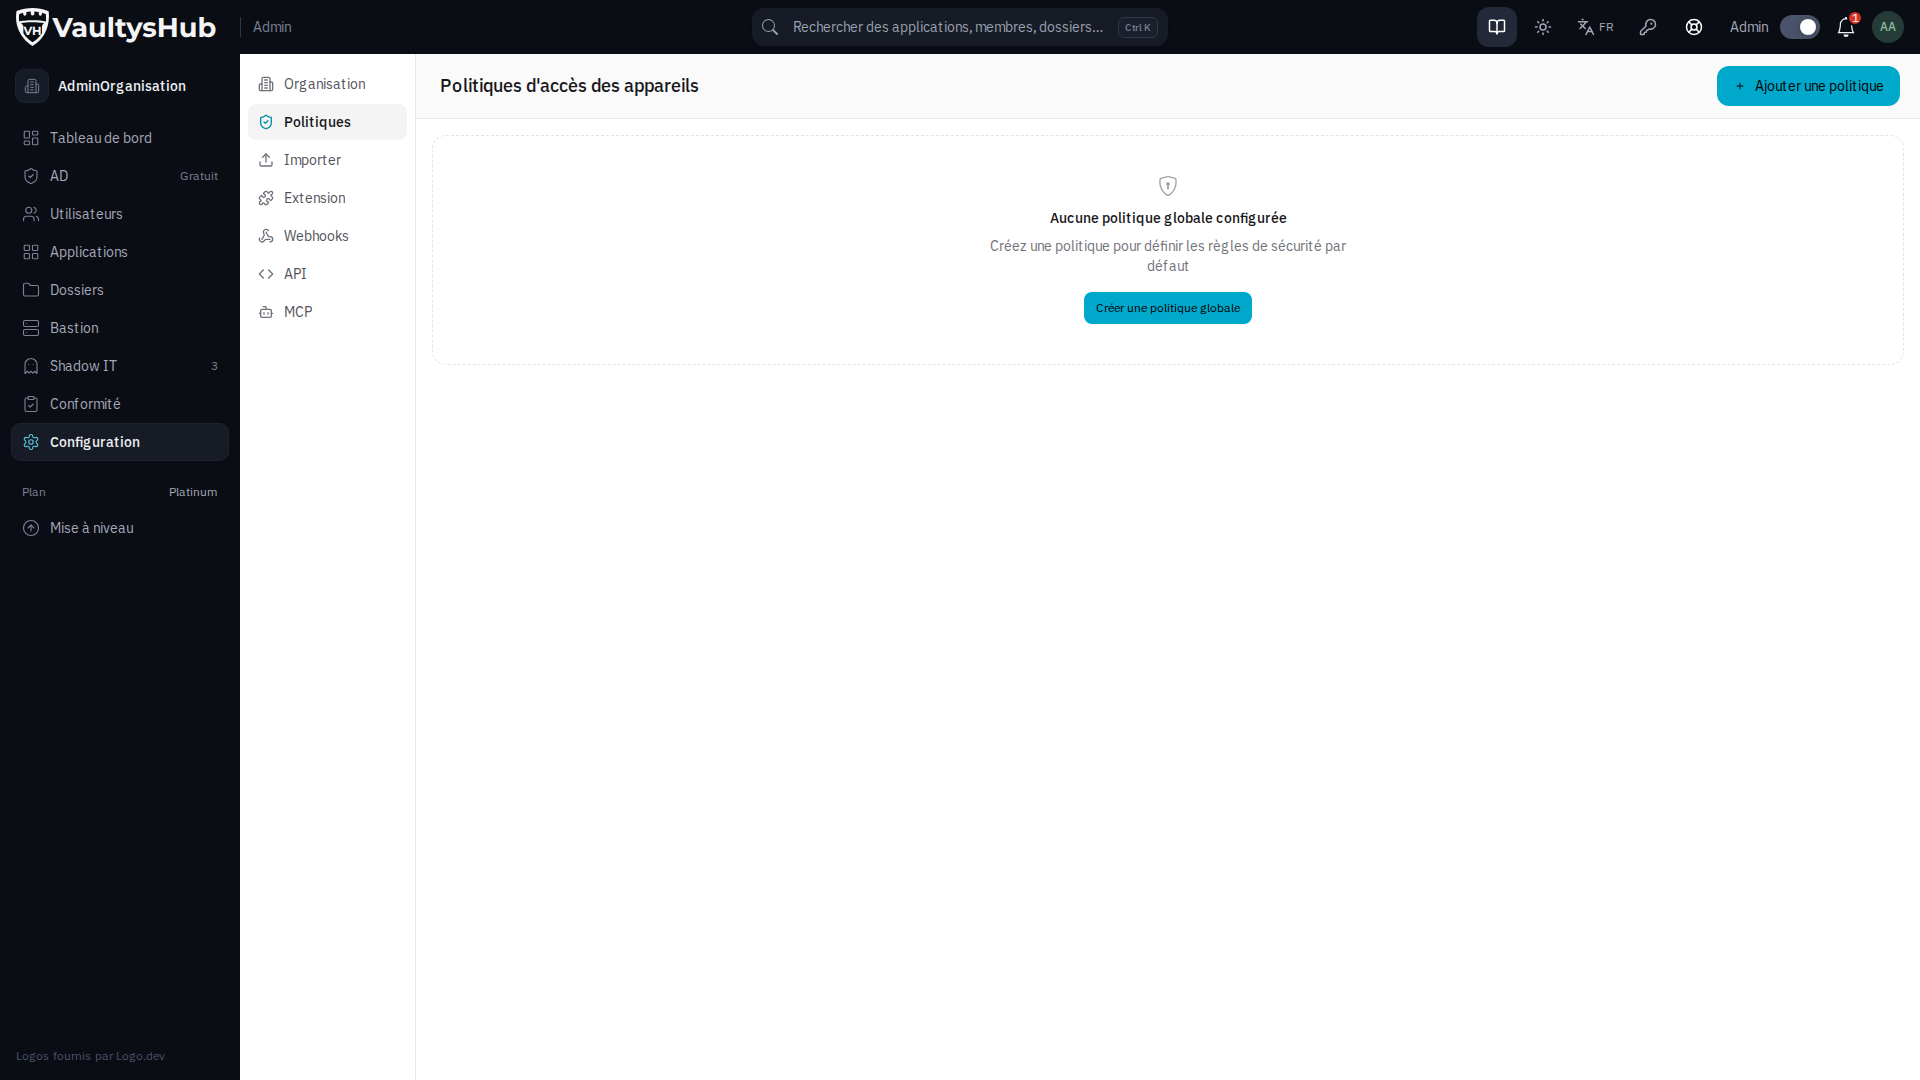
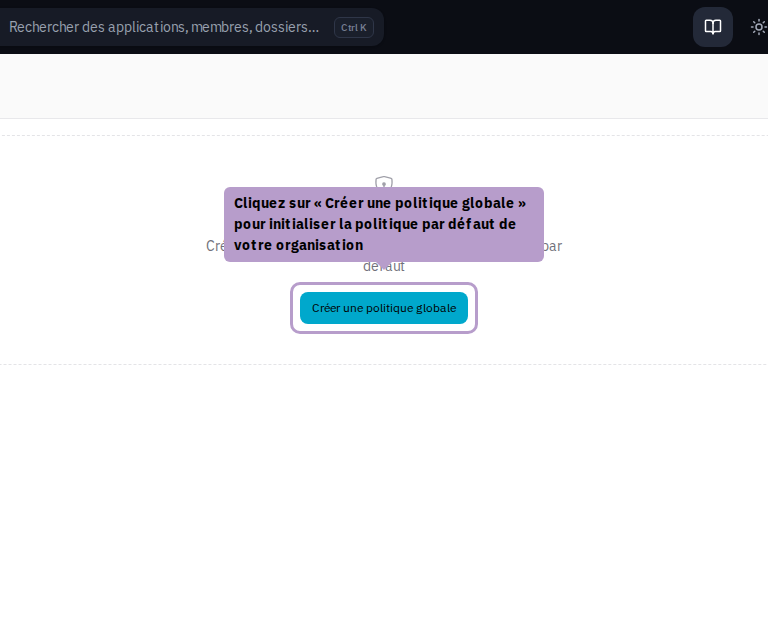
Global Policy
Upon first access, no policy is yet configured. Click the Create a Global Policy button to initialize the default policy applicable to all users.
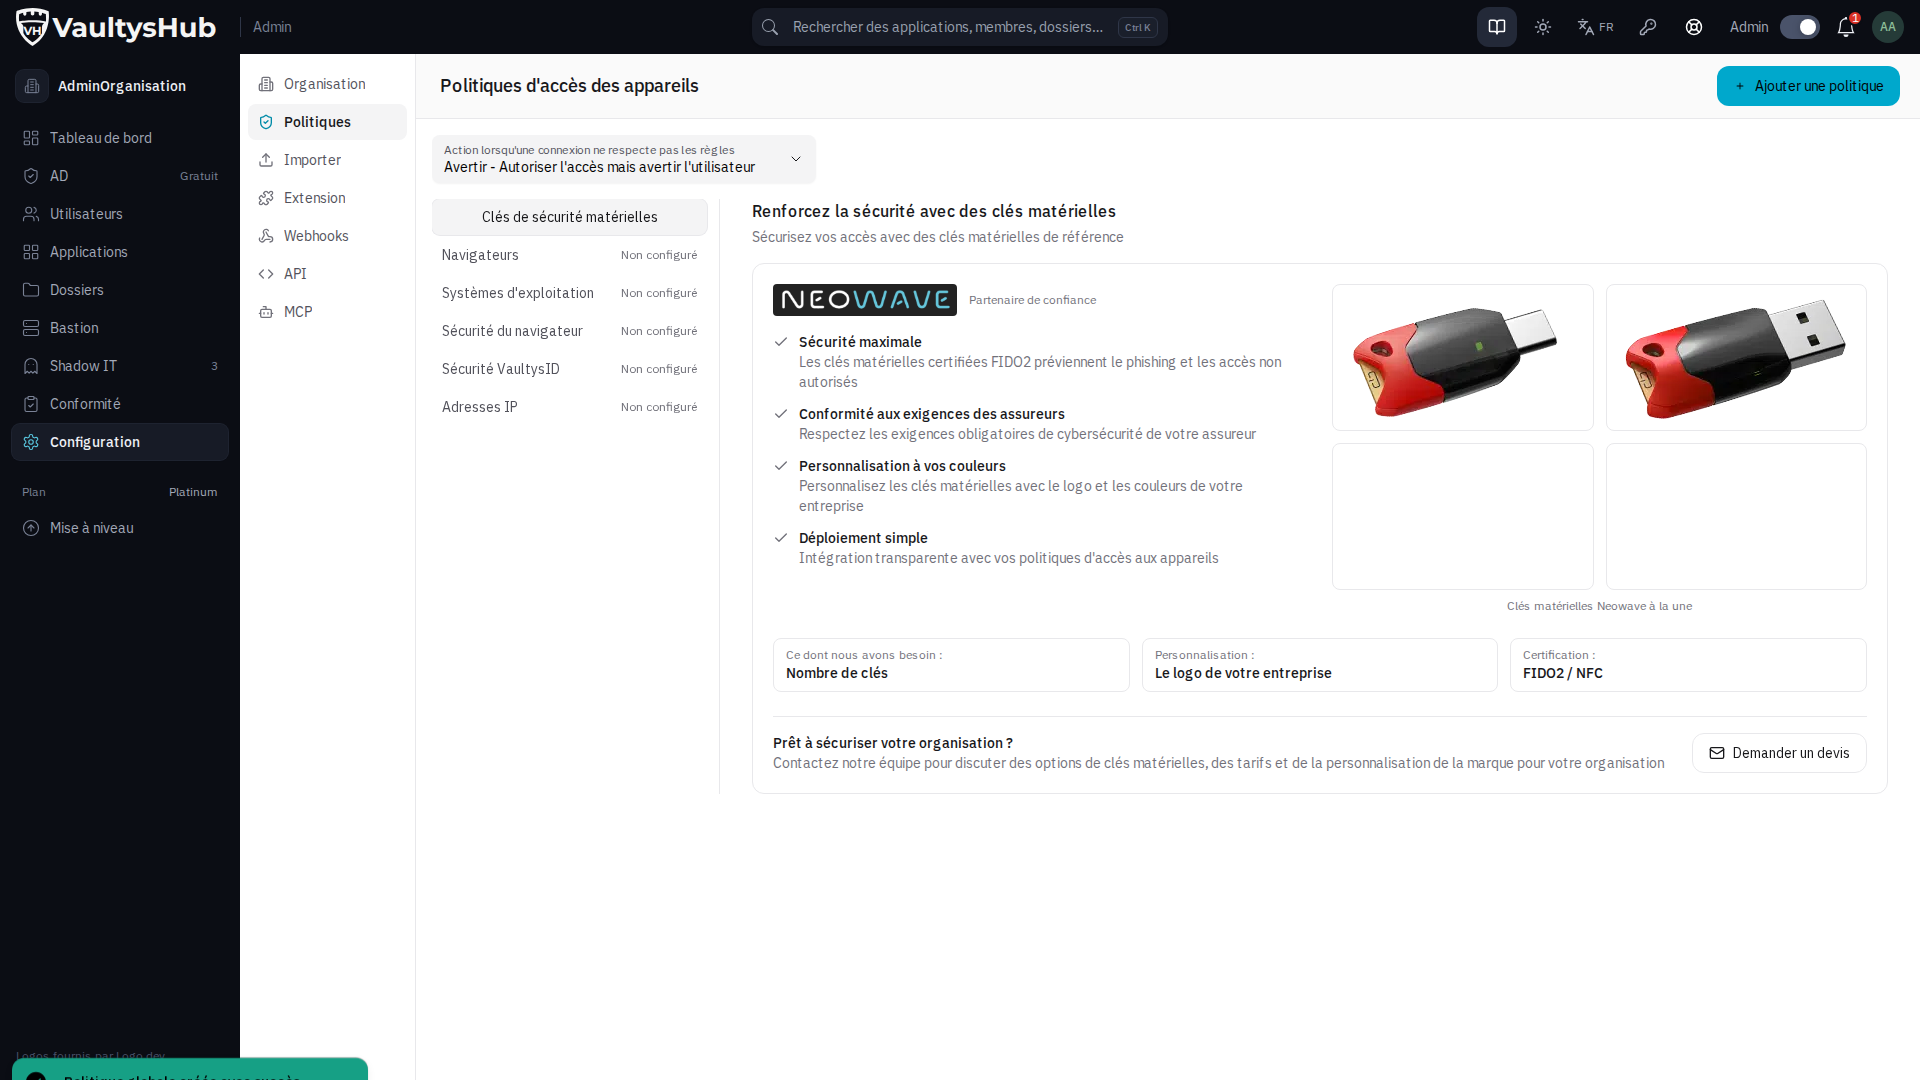
Configure a Policy
Once created, the policy appears in the editor. Each sidebar tab corresponds to a control dimension. The colored badges indicate the configuration status of each section.
Action on Violation
Define what should happen when a rule is not respected.
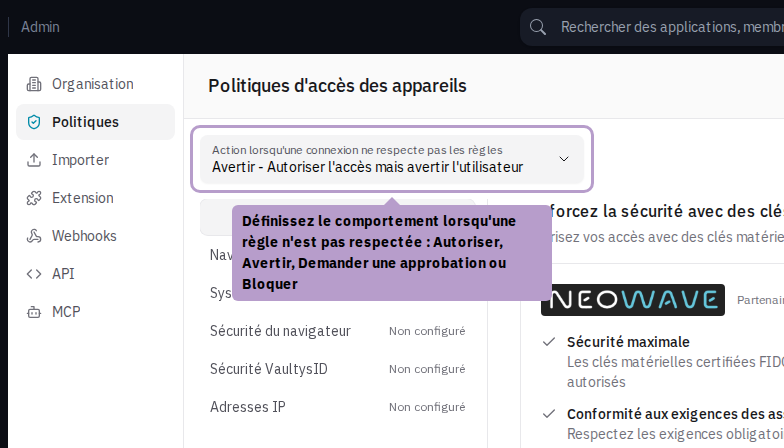
| Value | Behavior |
|---|---|
| Allow | Ignores the rules — no blocking |
| Warn | Allows access but informs the user |
| Admin Approval | Access is suspended until validated by an administrator |
| Block | Access denied |
Browsers Tab
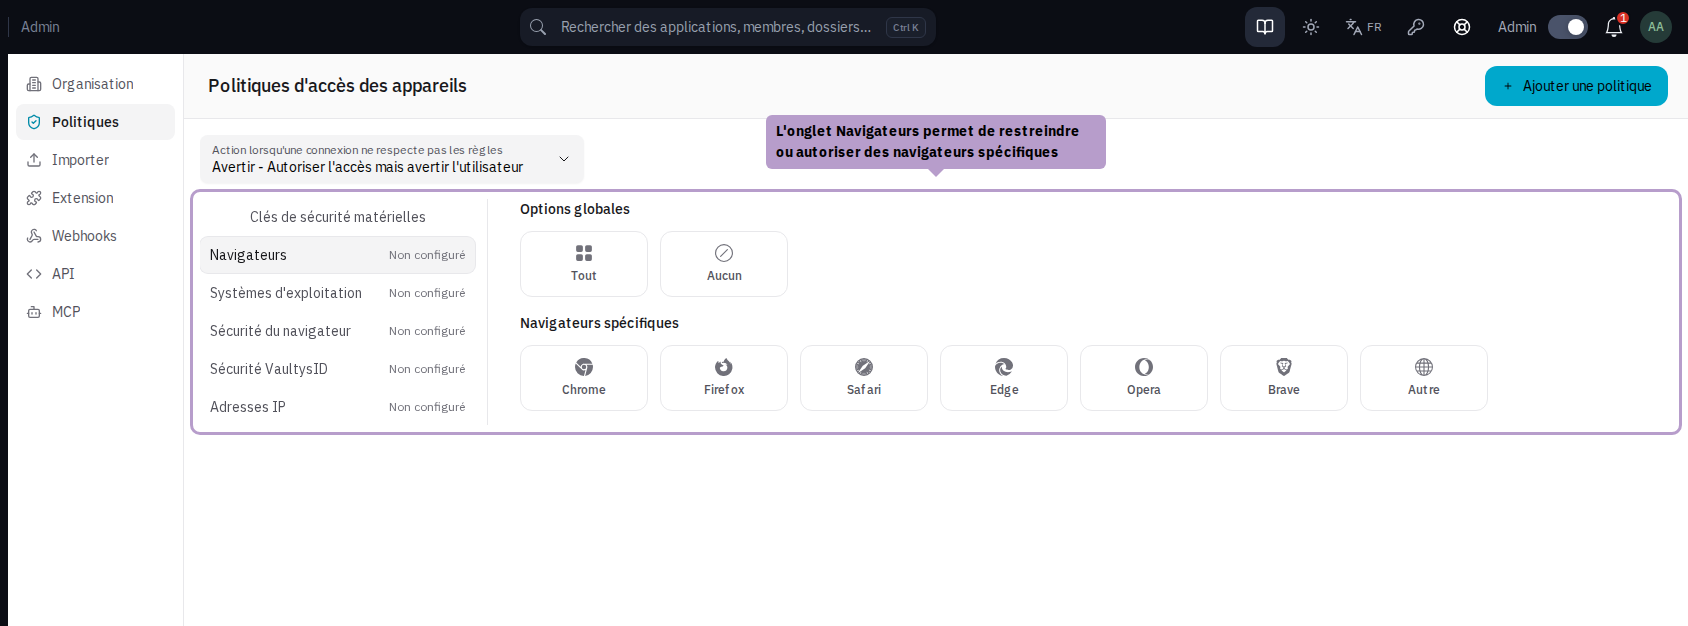
Allow or restrict access based on the browser used (Chrome, Firefox, Edge, Safari, Brave, Opera…). The options All and None apply a global rule.
Operating Systems Tab
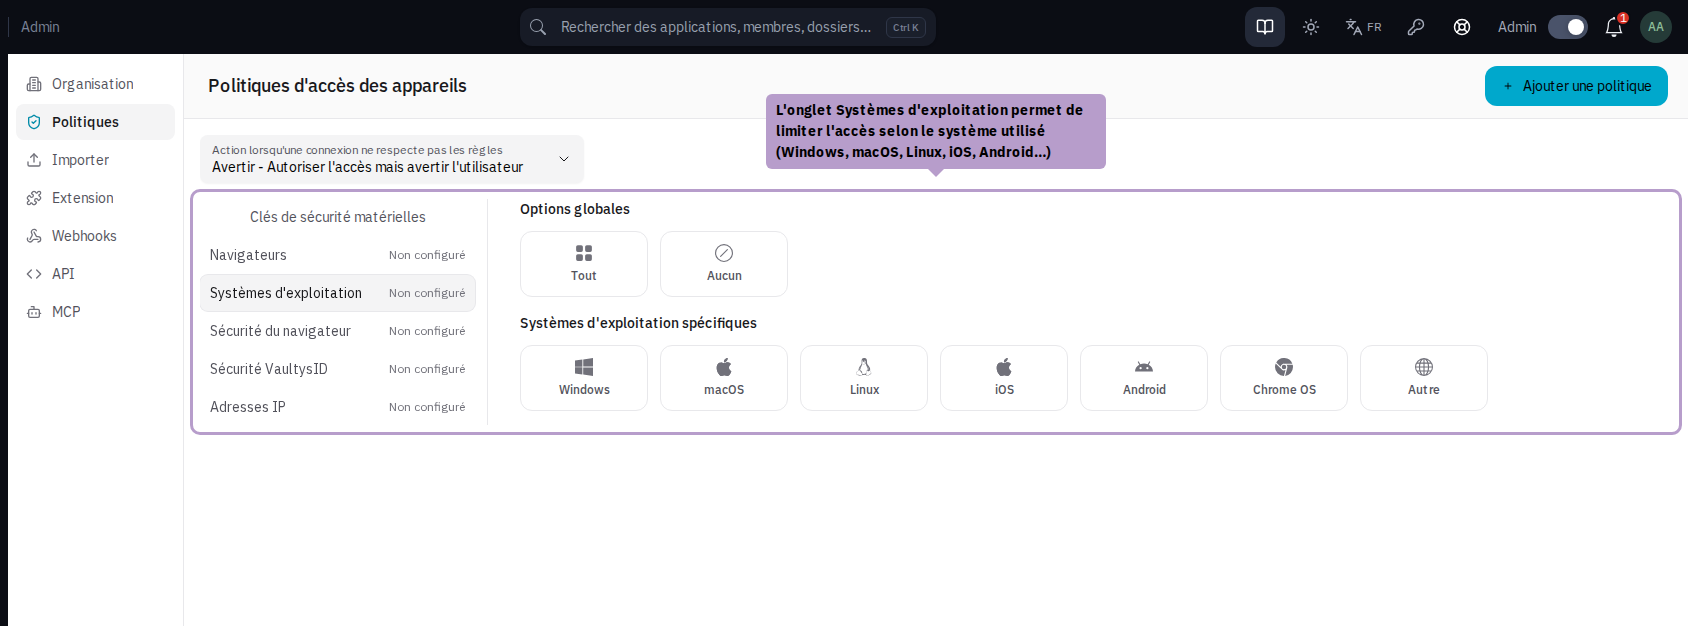
Limit access to the desired operating systems: Windows, macOS, Linux, iOS, Android, or Chrome OS.
Browser Security Tab
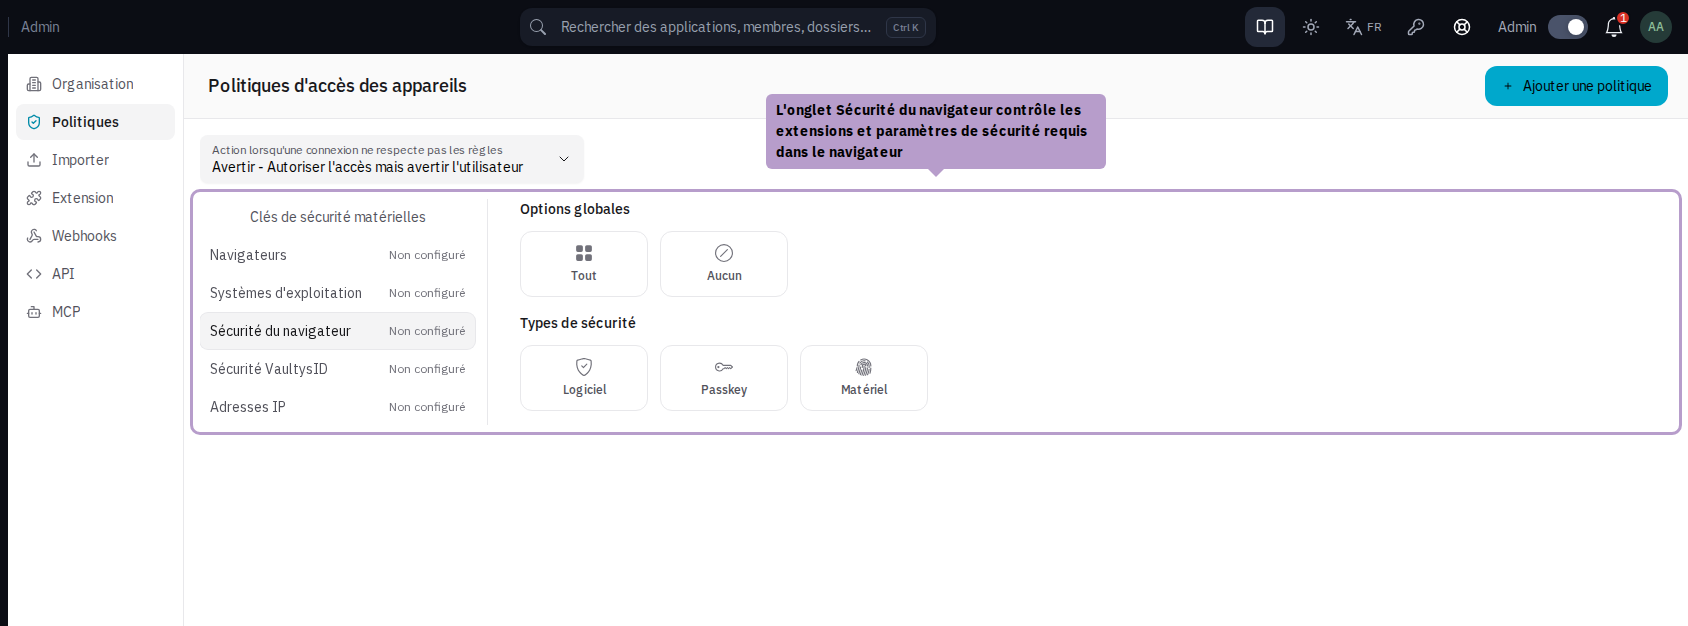
Define the requirements related to browser security (extensions, enabled settings).
VaultysID Security Tab
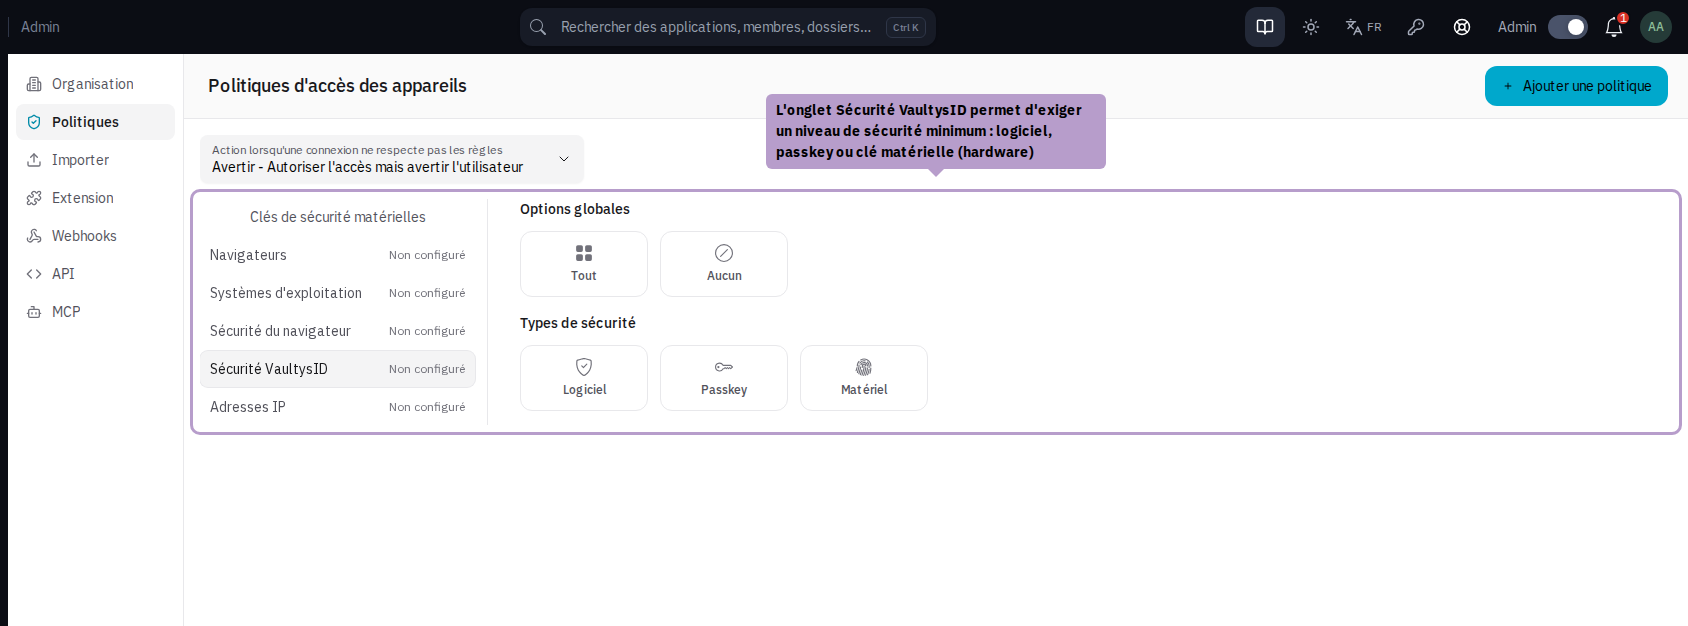
Require a minimum security level for the VaultysID identity:
- Software — key stored in software memory
- Passkey — authentication by passkey
- Hardware — physical security key (FIDO2 / CTAP2)
IP Addresses Tab
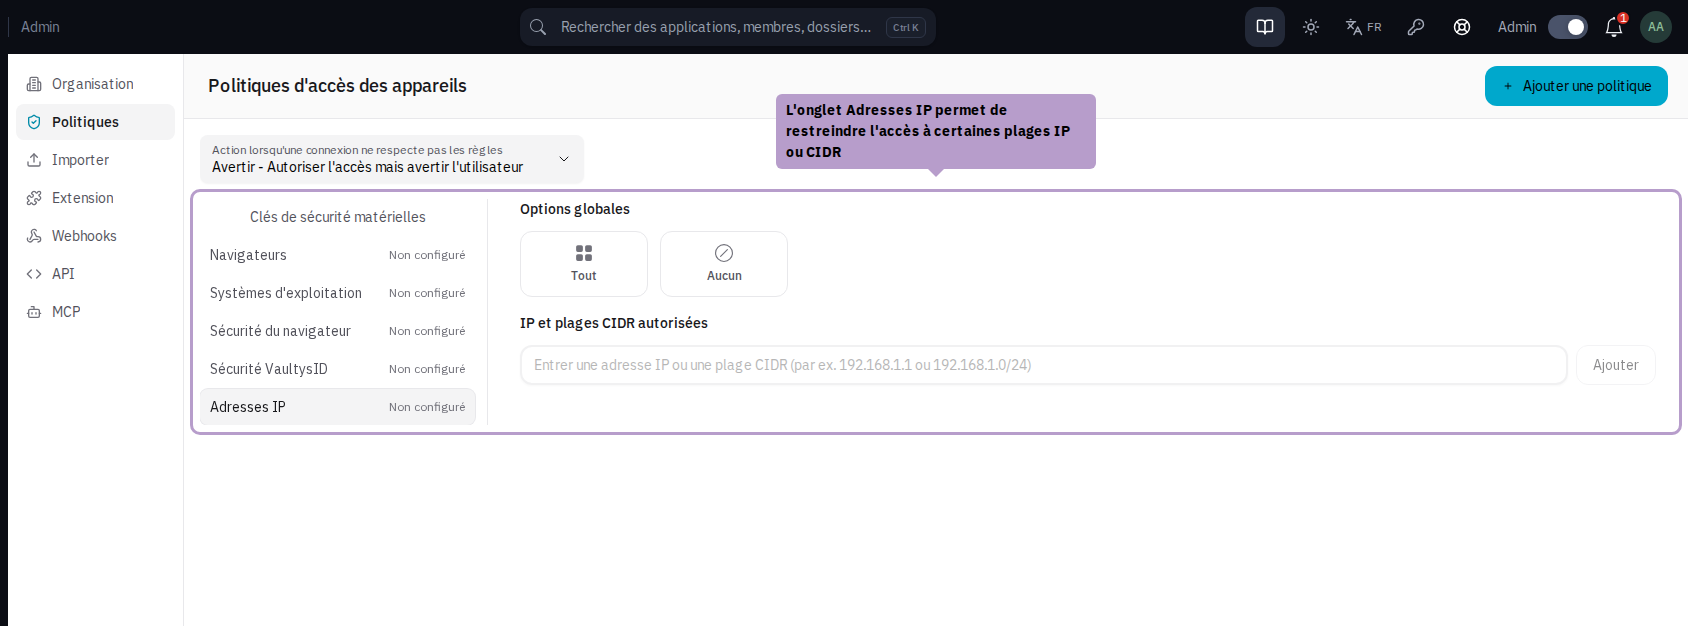
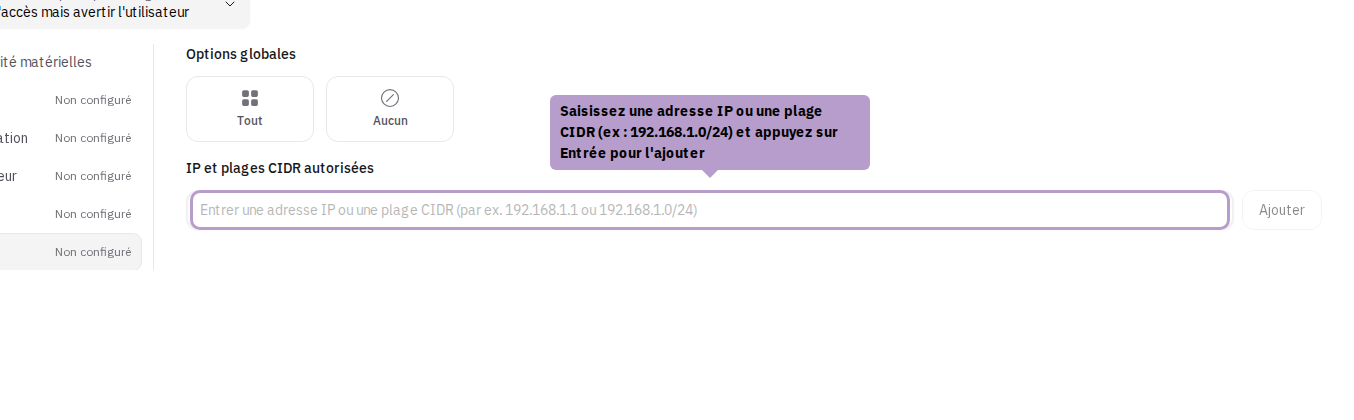
Specify the allowed IP addresses or CIDR ranges (e.g., 192.168.1.0/24). Only connections from these networks will be accepted.
Create Other Policies
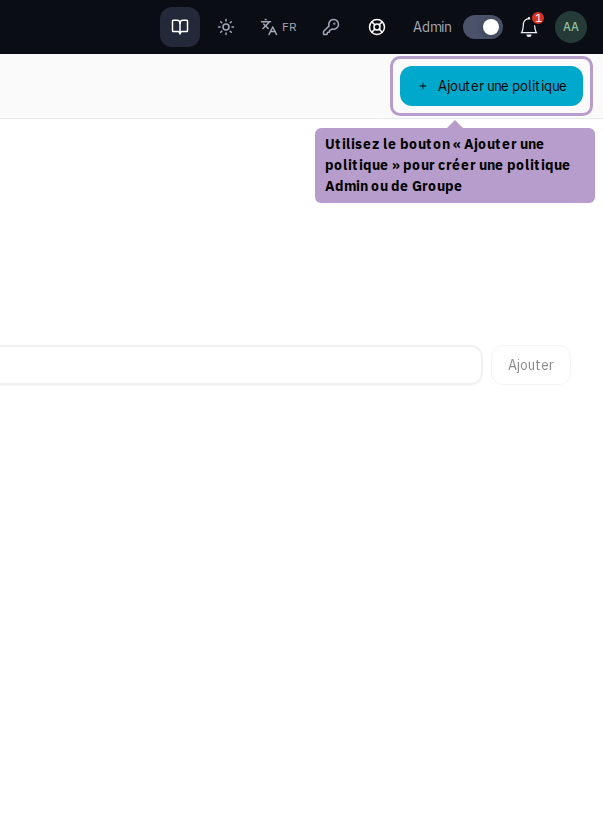
To create an Admin or Group policy, use the Add a Policy button in the toolbar.
A panel opens to choose the scope.
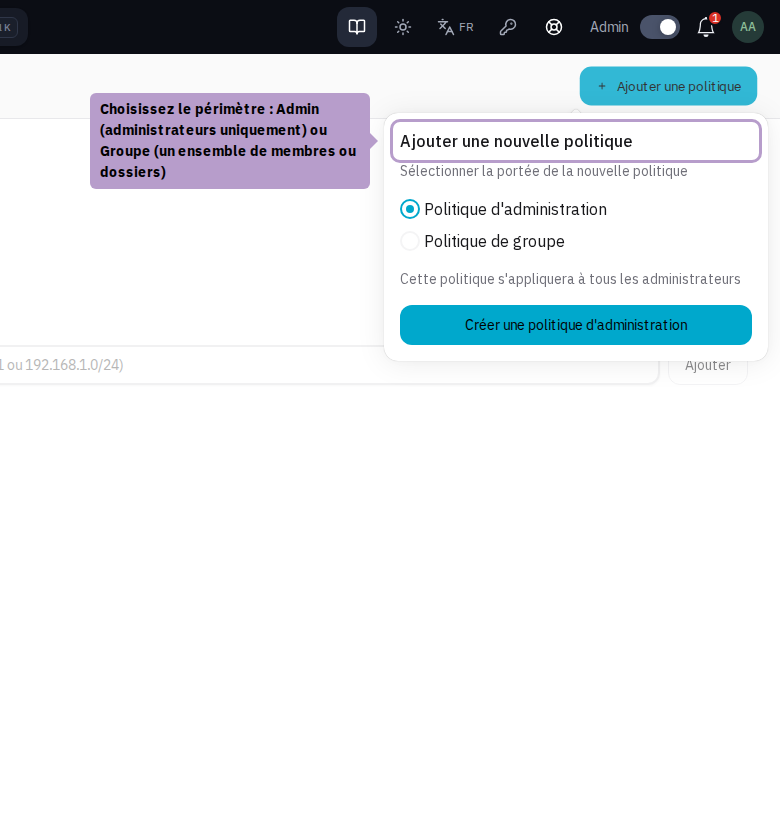
Admin Policy
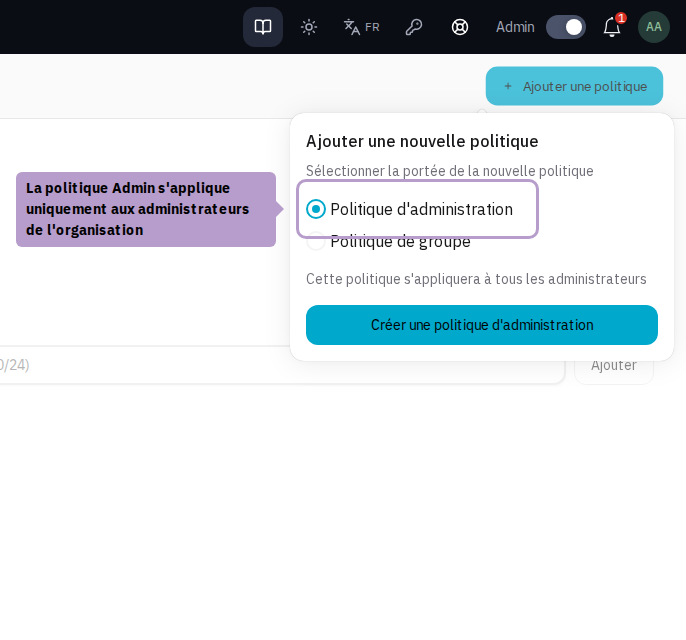
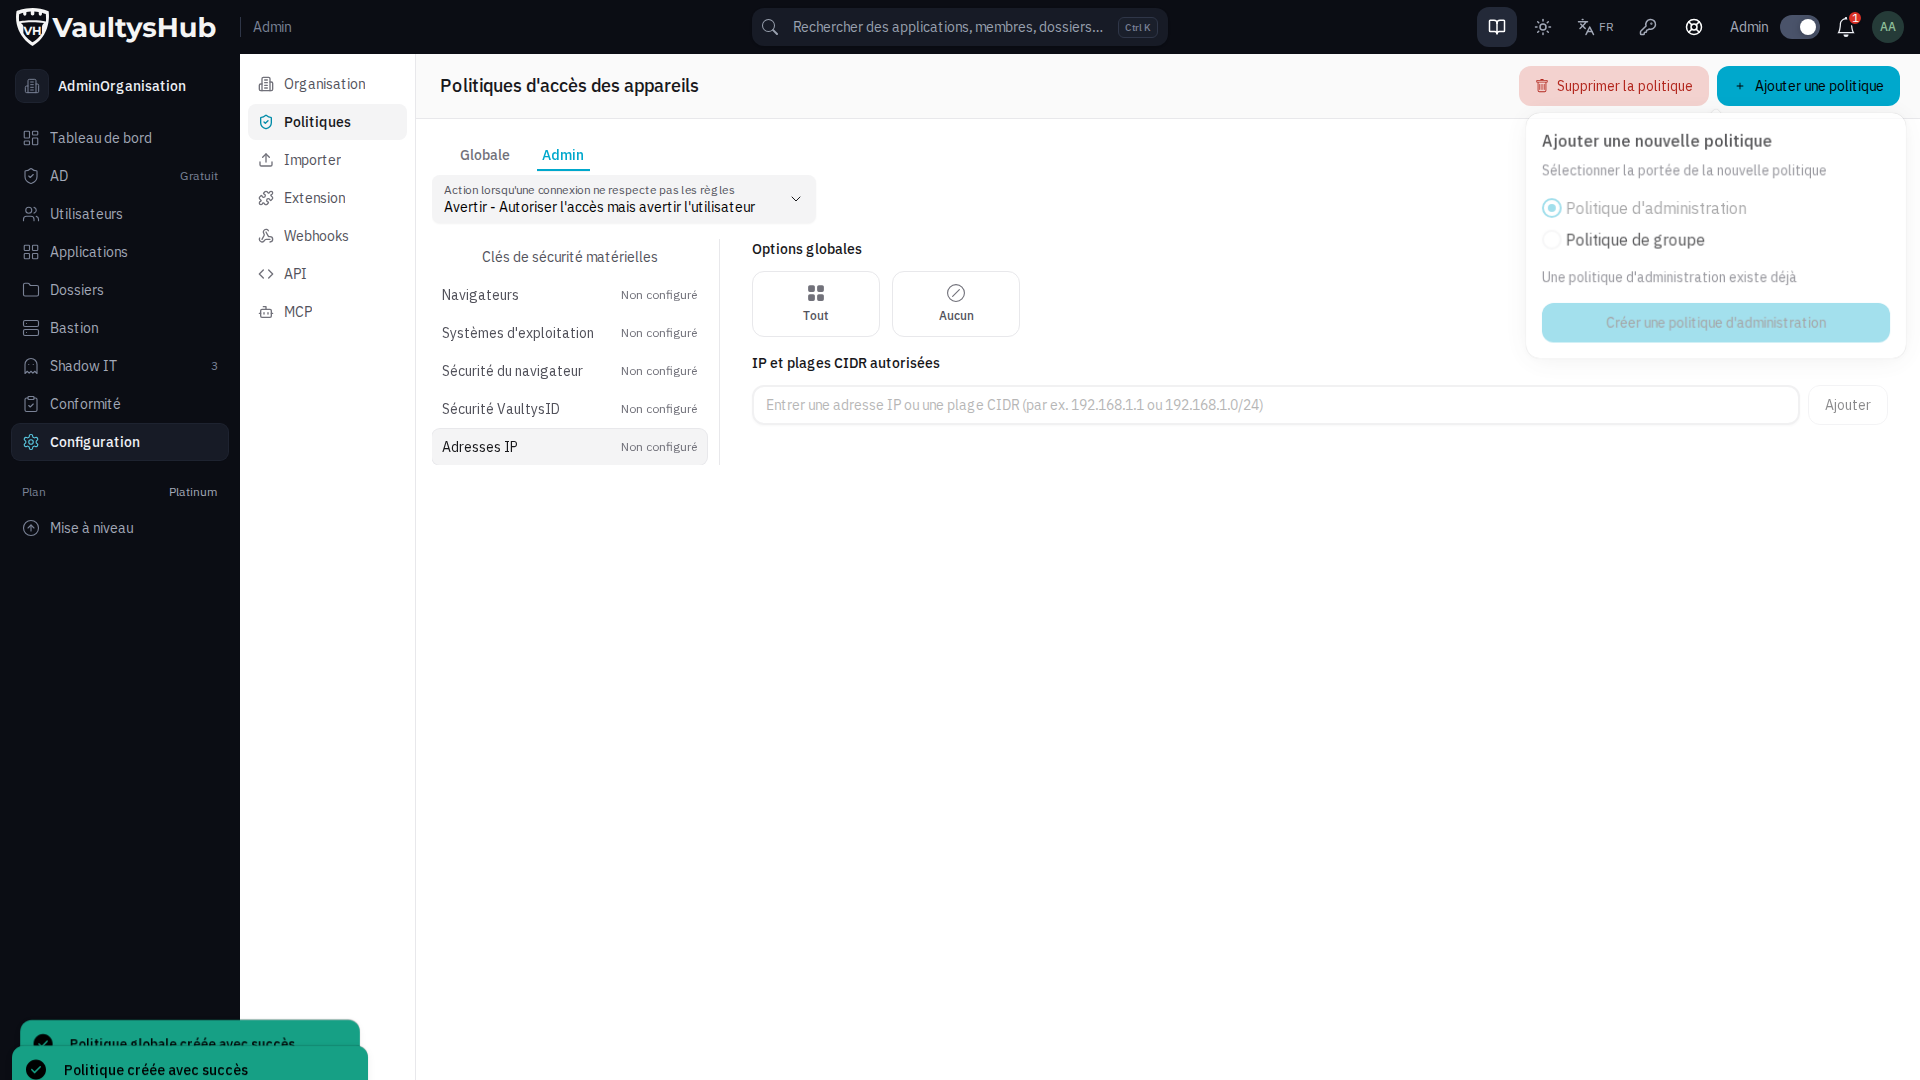
There can only be one Admin policy. The creation button will be disabled if it already exists.
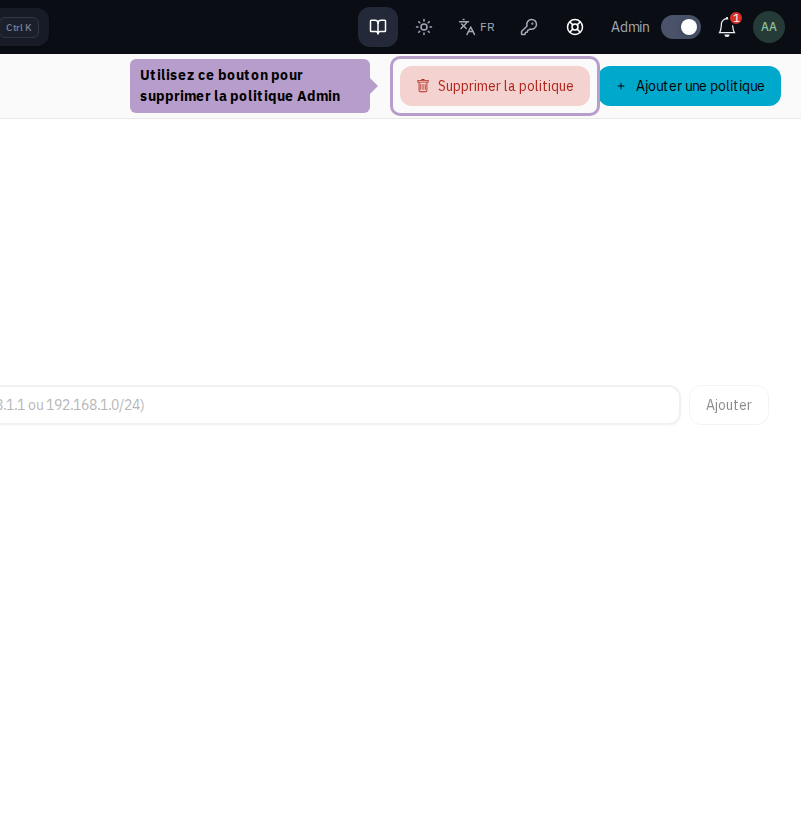
The Admin policy applies only to administrators. To delete it, use the Delete Policy button in the toolbar.
Group Policies
Group policies allow targeting a specific subset of users or folders with custom rules.
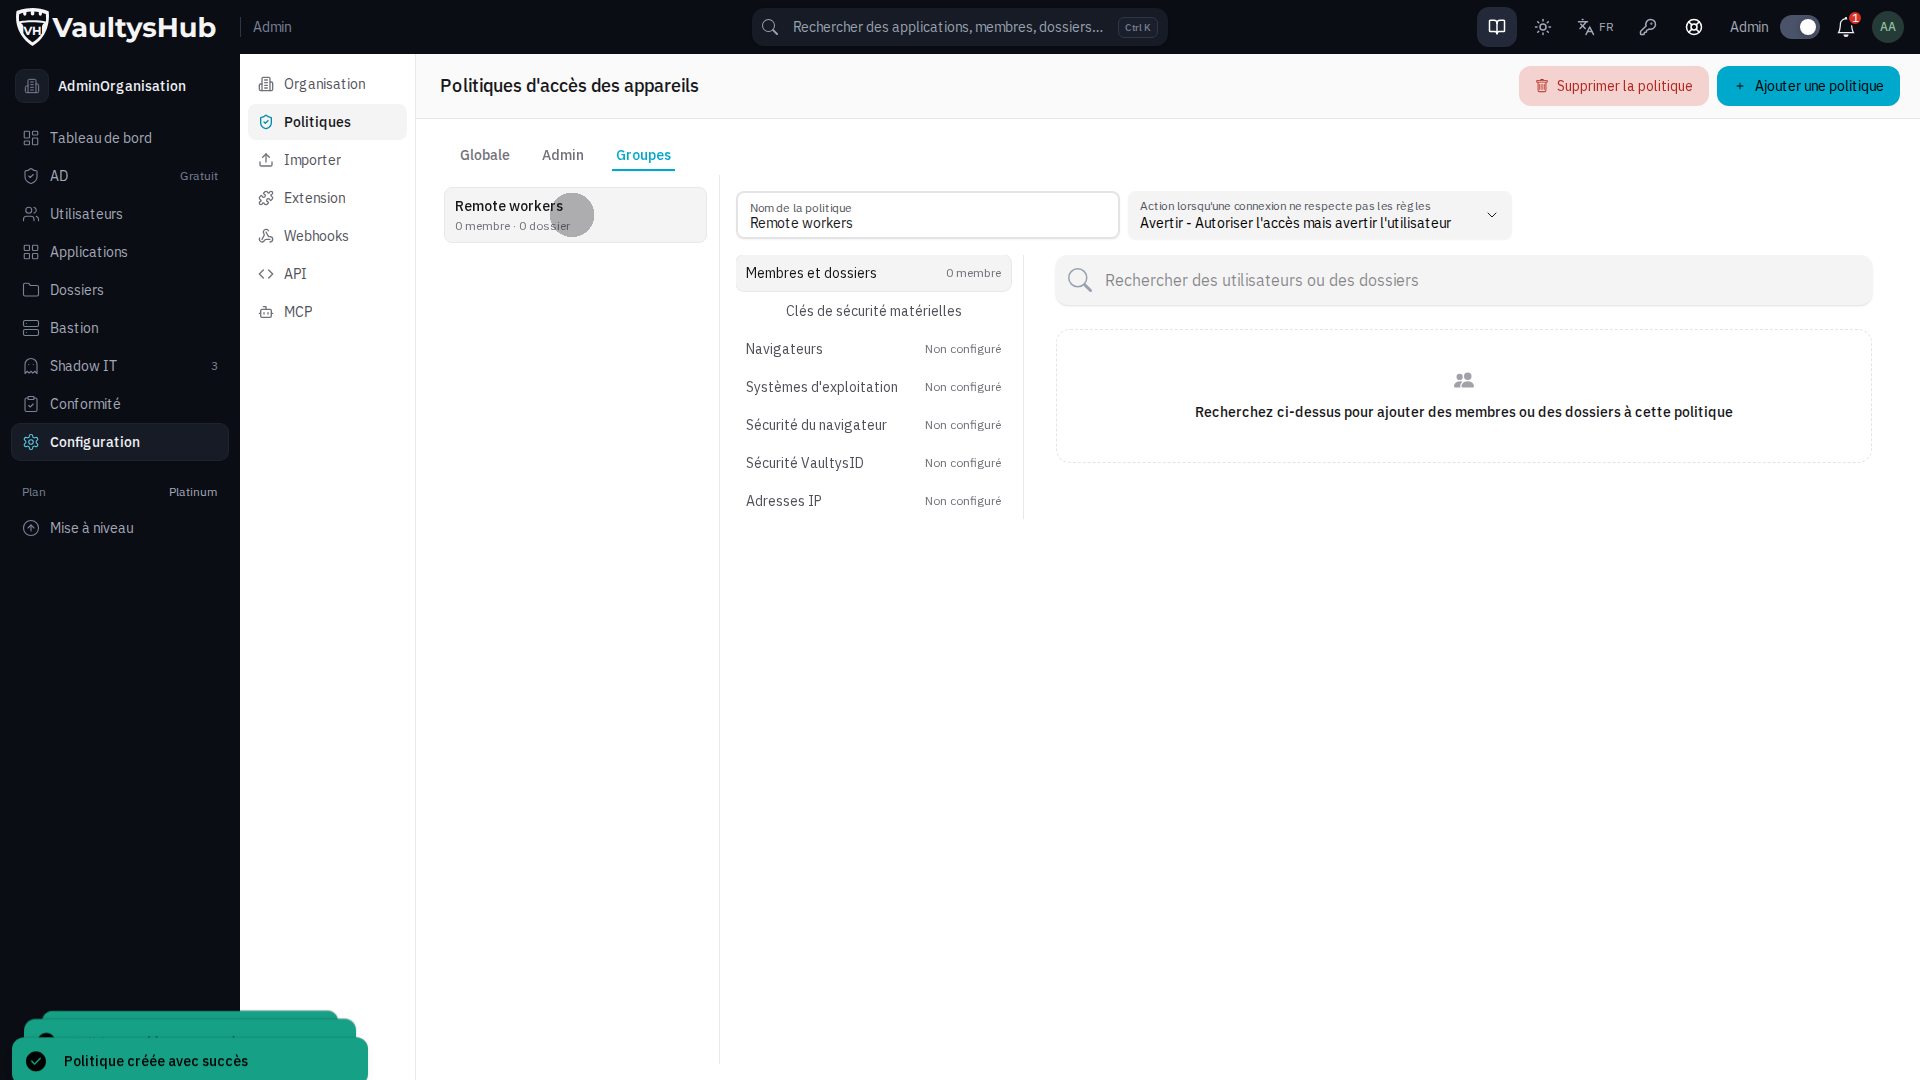
Select a group from the left column to access its editor.
Members & Folders
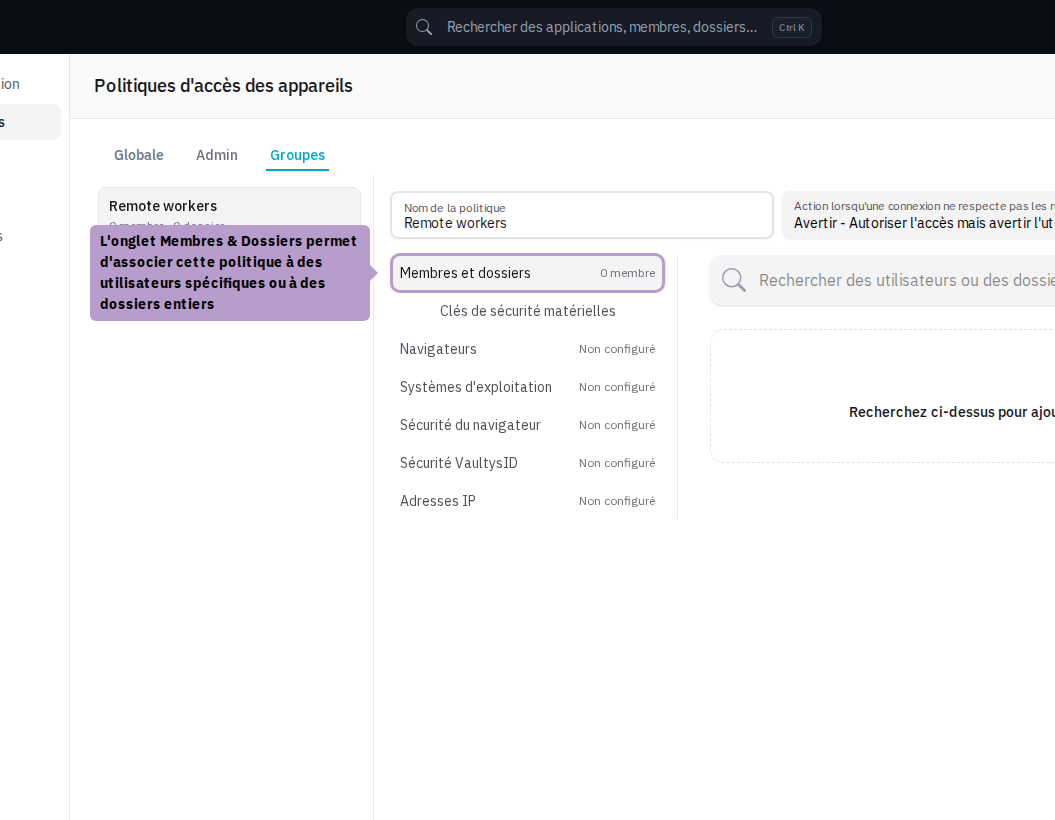
Associate the policy with individual users or entire folders. All members of the folder will be automatically covered.
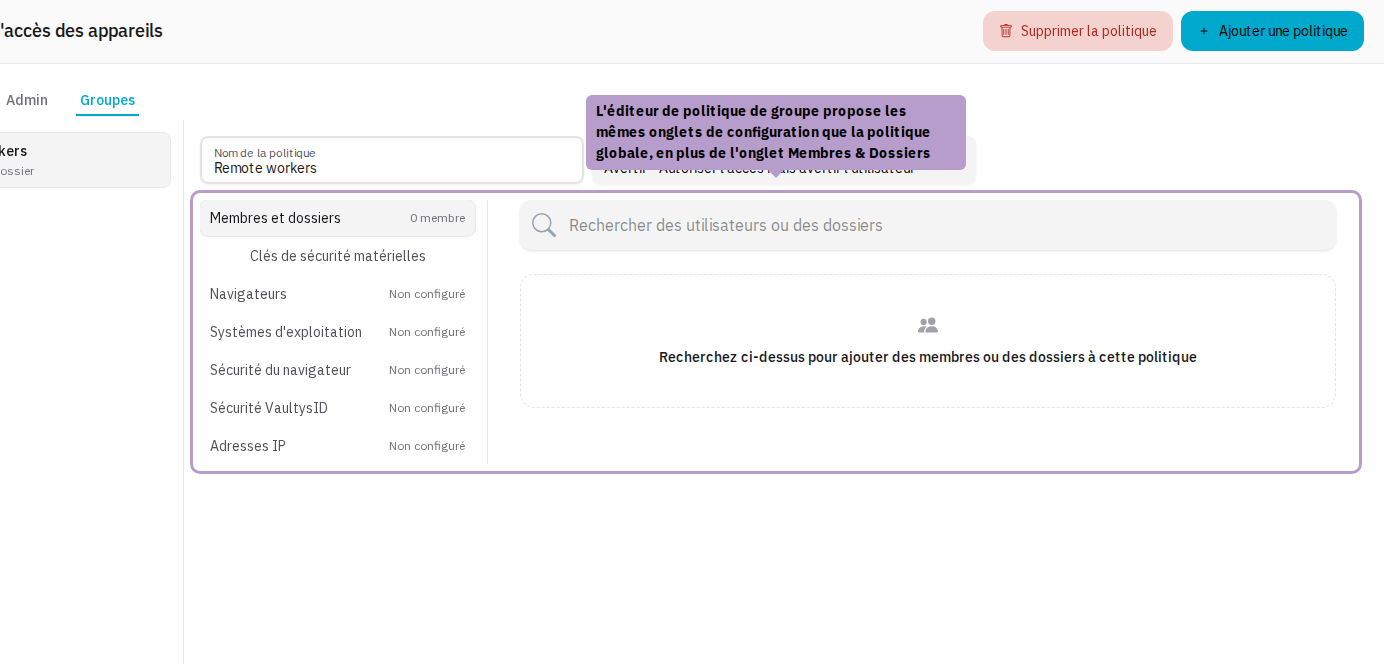
The rules of the group policy take precedence over the global policy for the affected users.