Reports
VaultysHub generates printable or downloadable PDF reports covering security, operations, and compliance. They are accessible from the Compliance menu, under the Reports tab.
Reports are part of the Compliance module. Without this module, the menu appears locked, with a presentation of the module. See Pricing and modules.
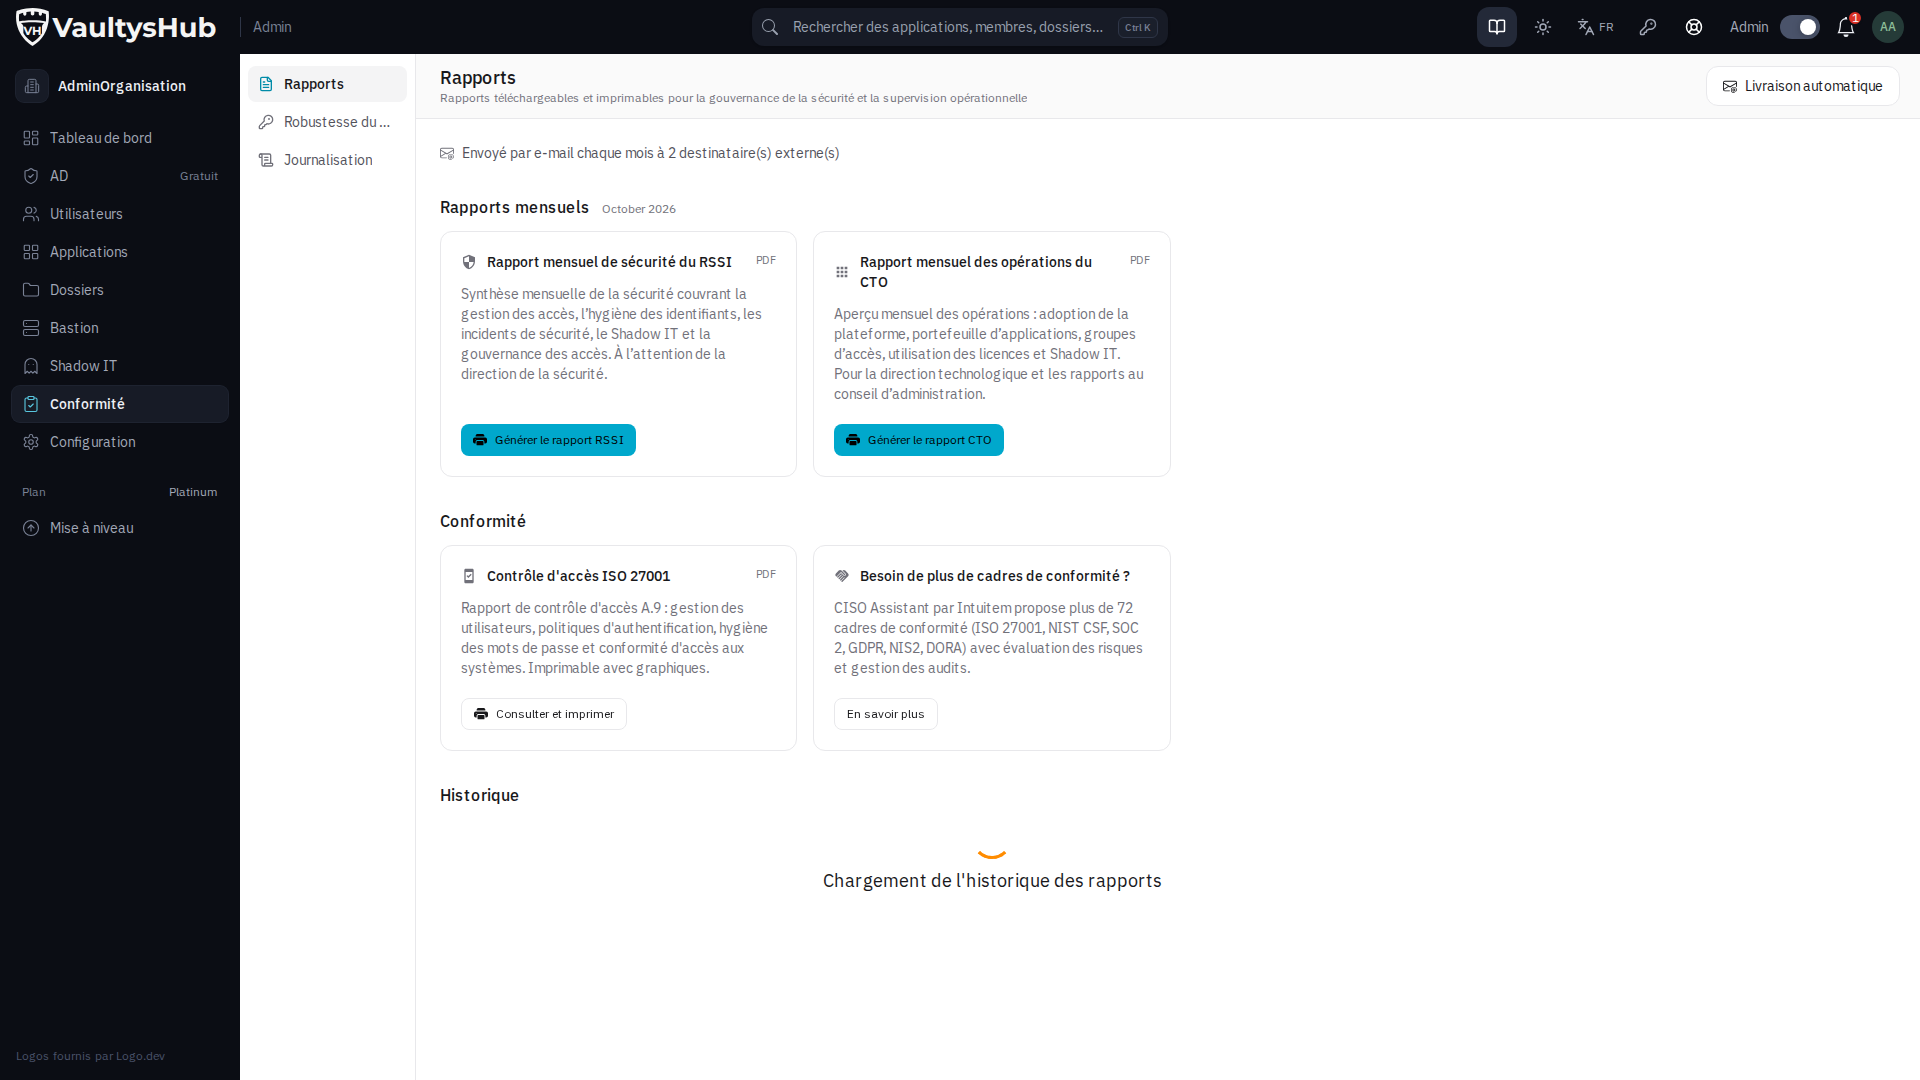
Monthly Reports
Monthly reports automatically cover the previous month and are intended for management.
CISO Report
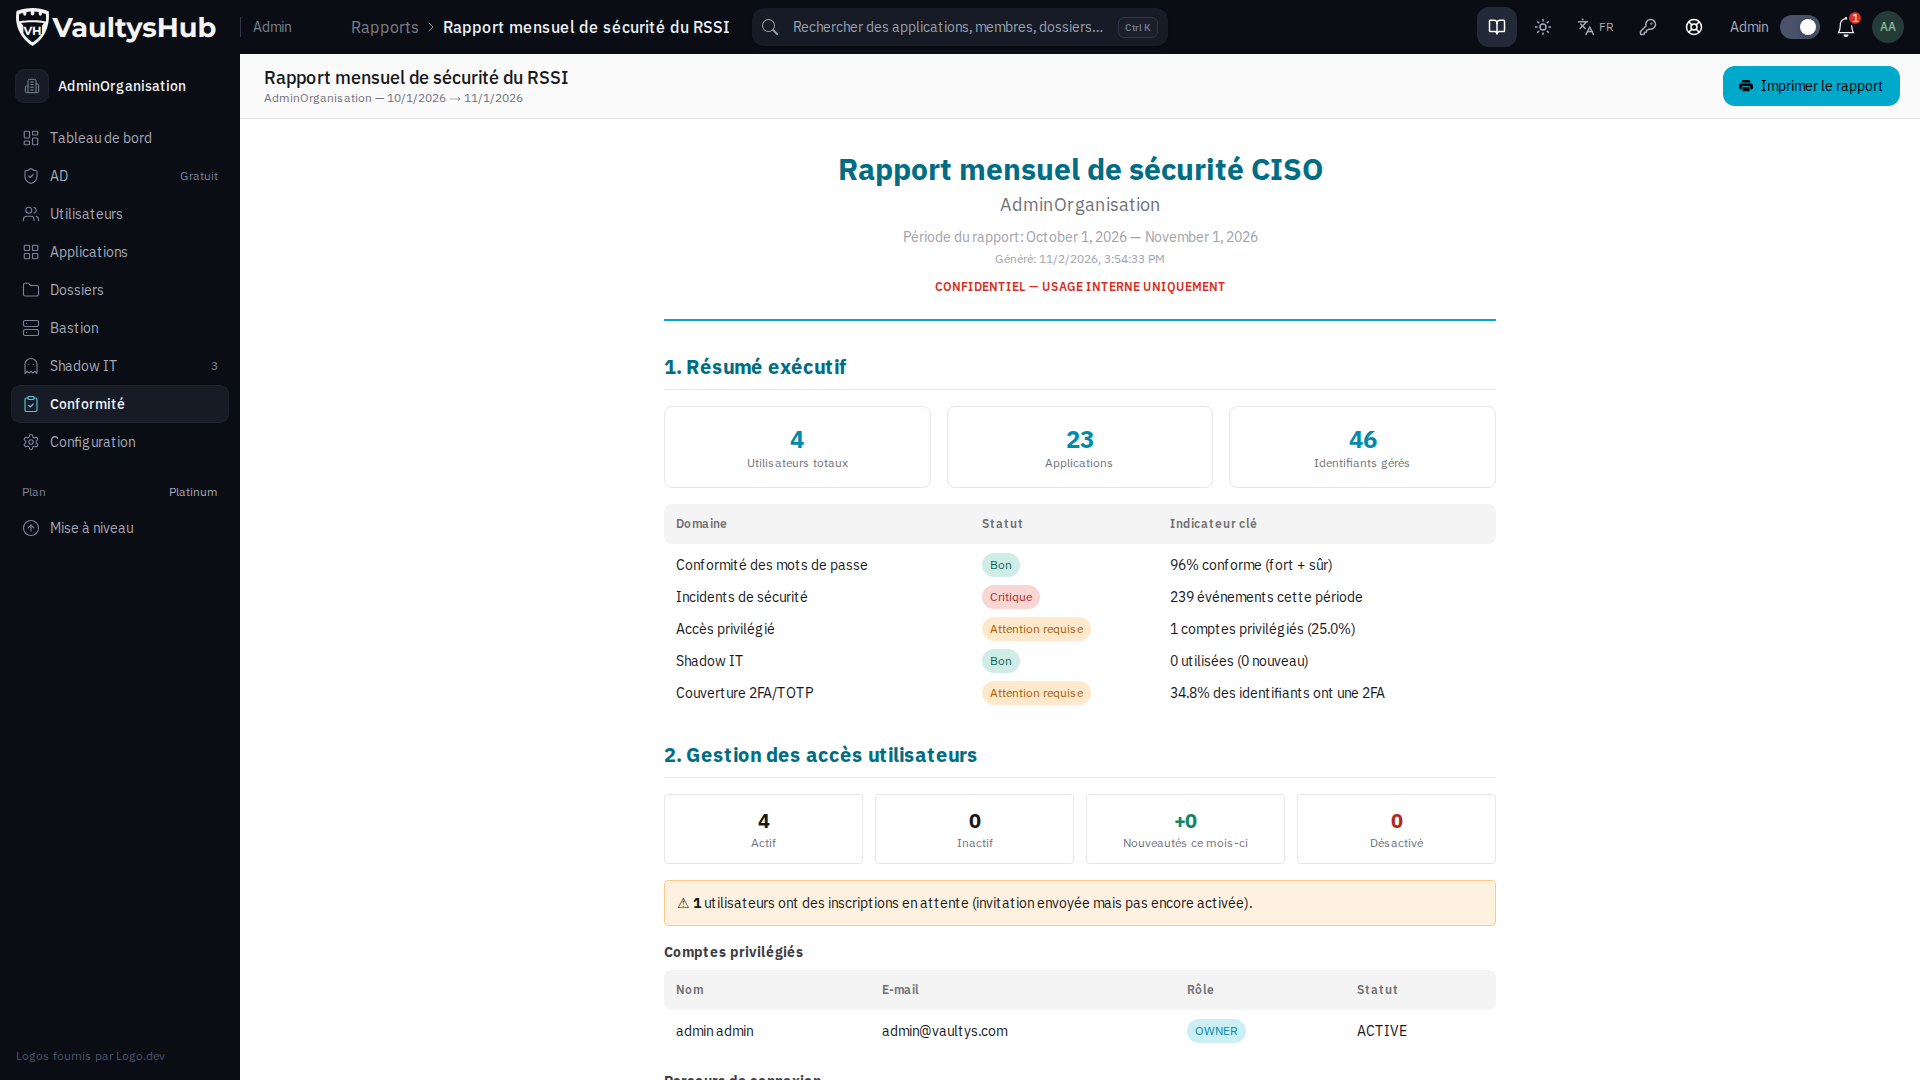
The CISO report (monthly security) covers the following topics:
- Access management and provisioning, with the sign-in journeys of the period
- Credential hygiene (password strength)
- Security incidents
- Shadow IT detections, with a map of accounts detected on Shadow IT applications (masked credentials)
- Access governance
Sign-in Journeys
The User Access Management section of the CISO report concludes with the Sign-in Journeys: the same Journey diagram as in the logging explorer, calculated over the reporting period.
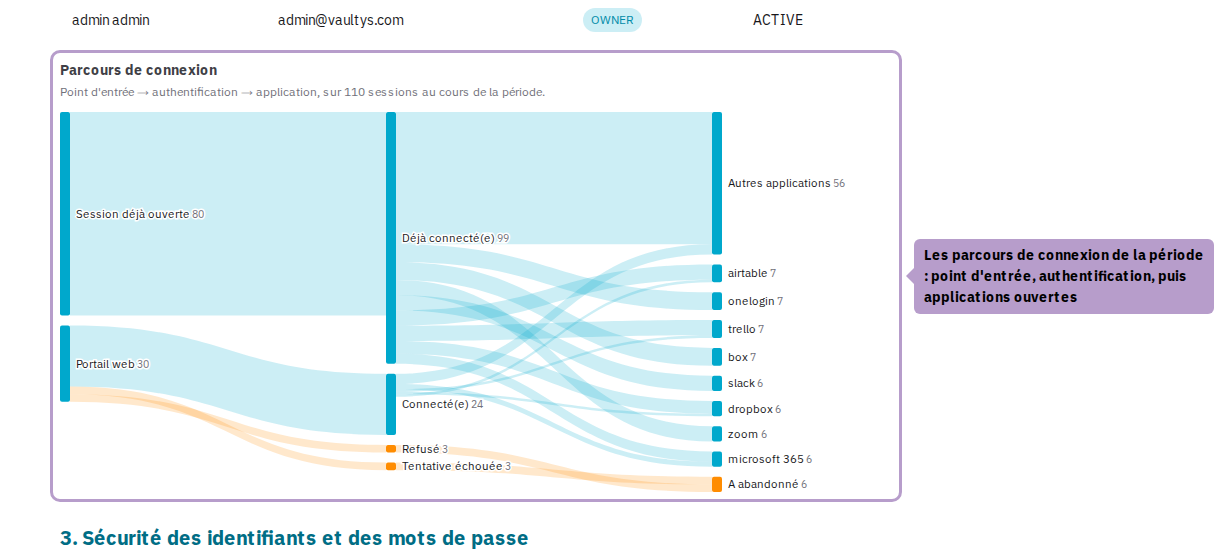
Each session is tracked across three columns, the thickness of a band being proportional to the number of sessions:
- Entry Point — Web Portal, Browser Extension, Windows Login, Linux Login, or Session already open when an application was opened without prior login during the period.
- Authentication — Logged In, Failed Attempt, Denied, or Already Logged In.
- Applications opened afterwards (the most used individually, others grouped under Other Applications); after a failure, Tried Again, then Logged In or Gave Up.
The text above the diagram indicates the number of sessions during the period. In a very large organization, only the most recent events are considered, which the report notes. This section does not appear if no logins or application openings were recorded during the period.
The report presents a snapshot overview. To filter individuals who went through a step or to track the detailed journey of a person, use the Logging explorer.
CTO Report
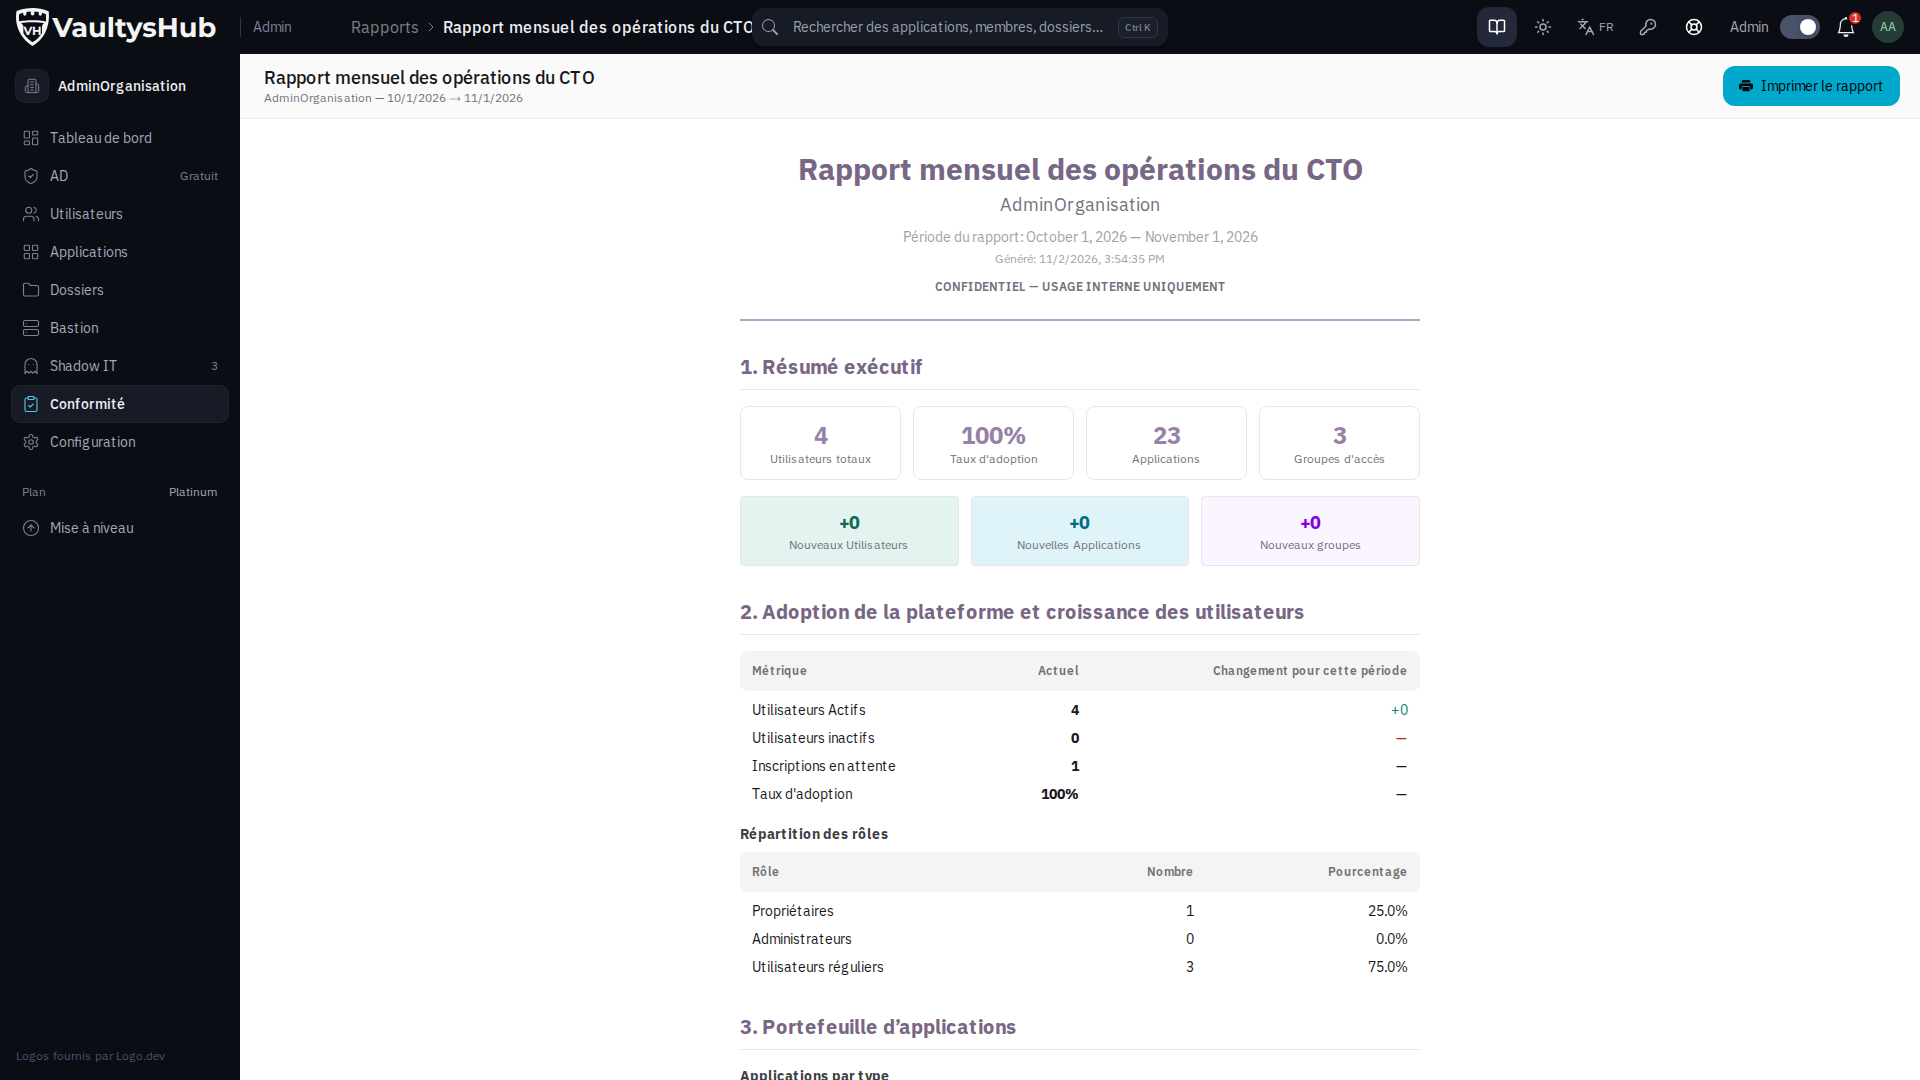
The CTO report (monthly operations) covers:
- Platform adoption
- Application portfolio
- Access groups and folders
- License usage
- Shadow IT
Compliance
ISO 27001 — Access Control
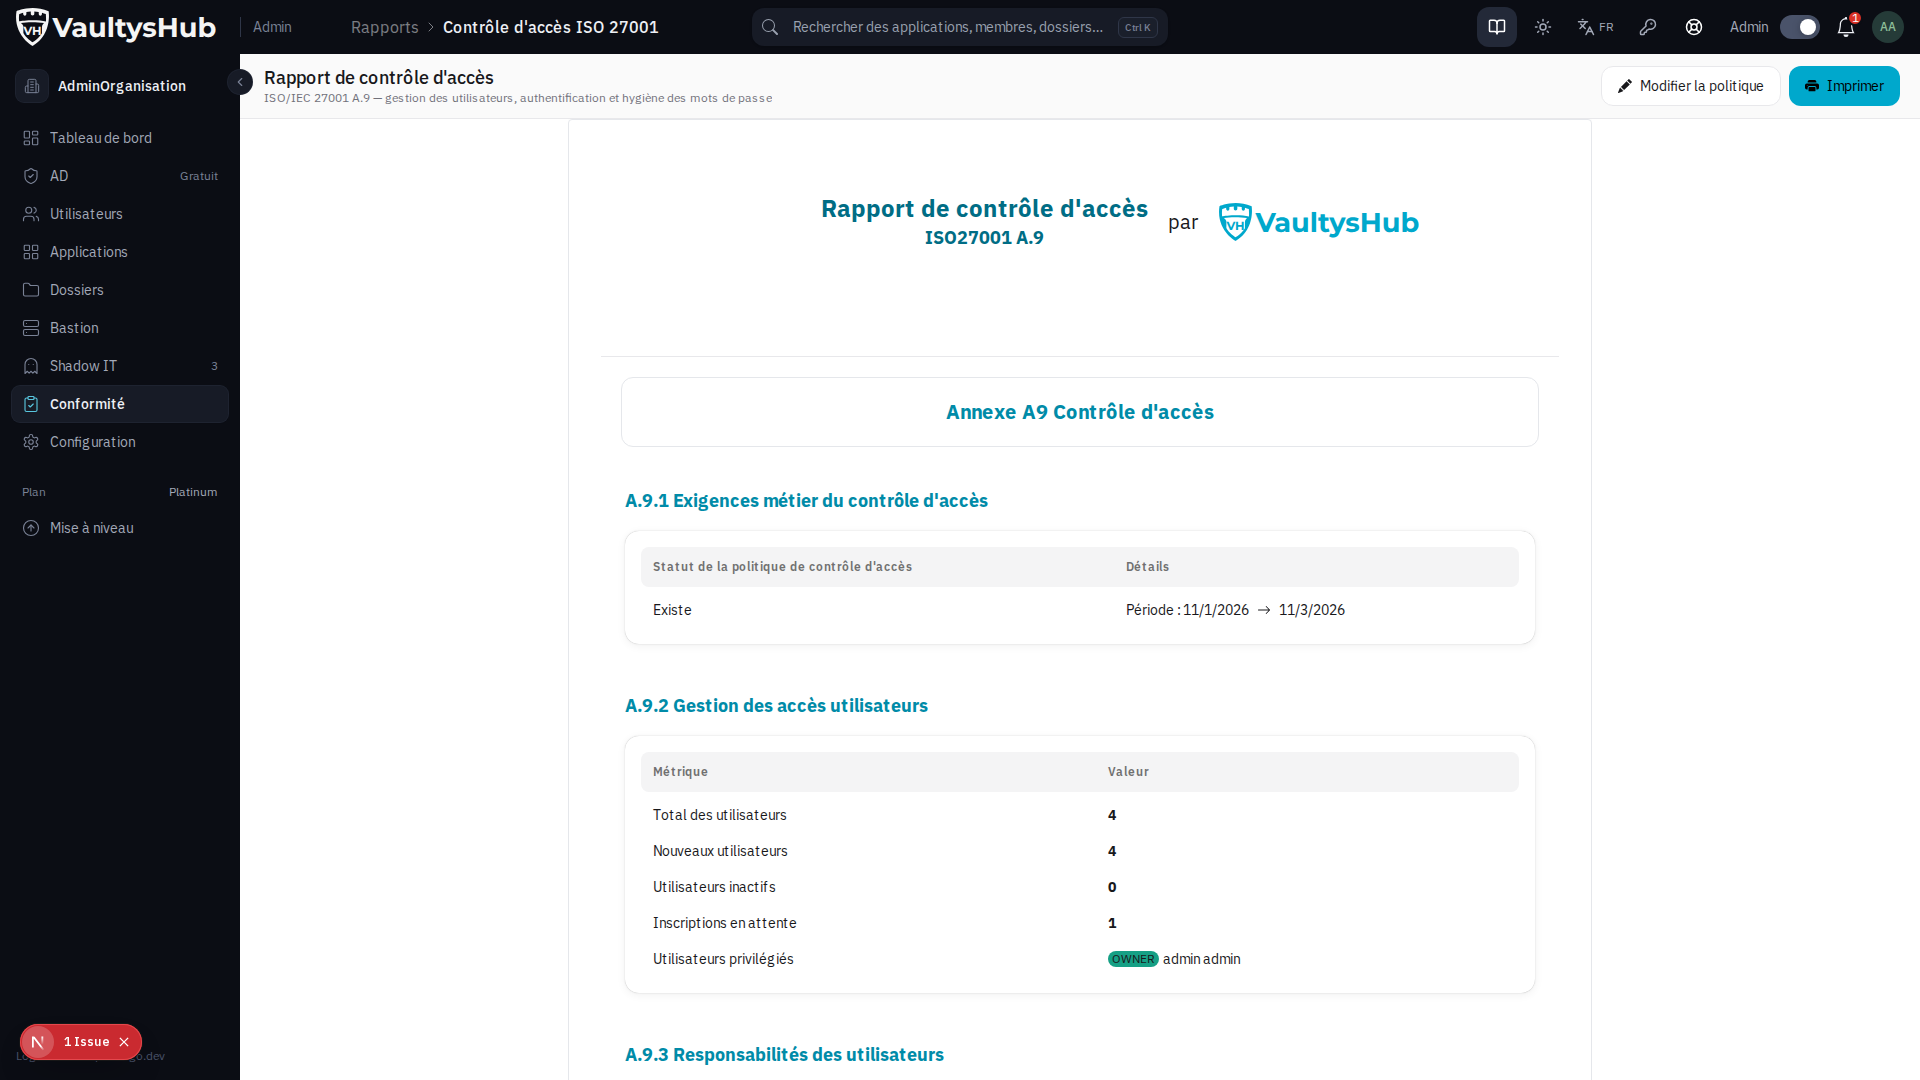
The ISO 27001 A.9 report is printable with graphs. It details:
- User provisioning and de-provisioning
- Applied authentication policies
- Password hygiene
- Compliance of access rights to systems
To access additional compliance frameworks (NIST CSF, SOC 2, GDPR, NIS2, DORA…), VaultysHub offers integration with CISO Assistant from Intuitem, accessible from the Need more frameworks? section of the Reports menu.