SSO Configuration
VaultysHub acts as an identity provider (IdP) and supports two SSO protocols: SAML 2.0 and OpenID Connect (OIDC). Your external applications delegate authentication to VaultysHub — your users log in once and access all their applications.
Accessing Authentication Configuration
From the list of applications, open the action menu of an application, then click on Edit.
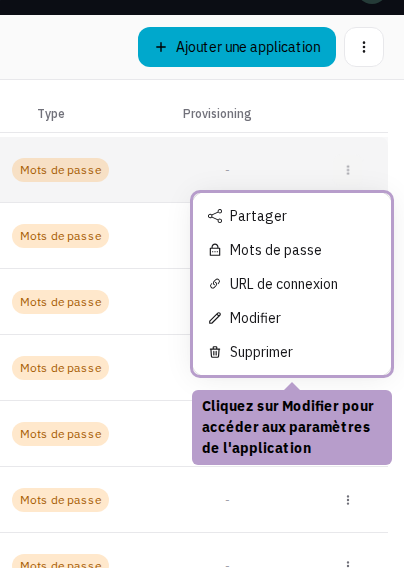
On the application page, select the Authentication tab. Then choose the desired protocol from the dropdown menu: SAML2 or OIDC.
SAML 2.0 Configuration
Select SAML2 from the dropdown menu to enable this protocol.
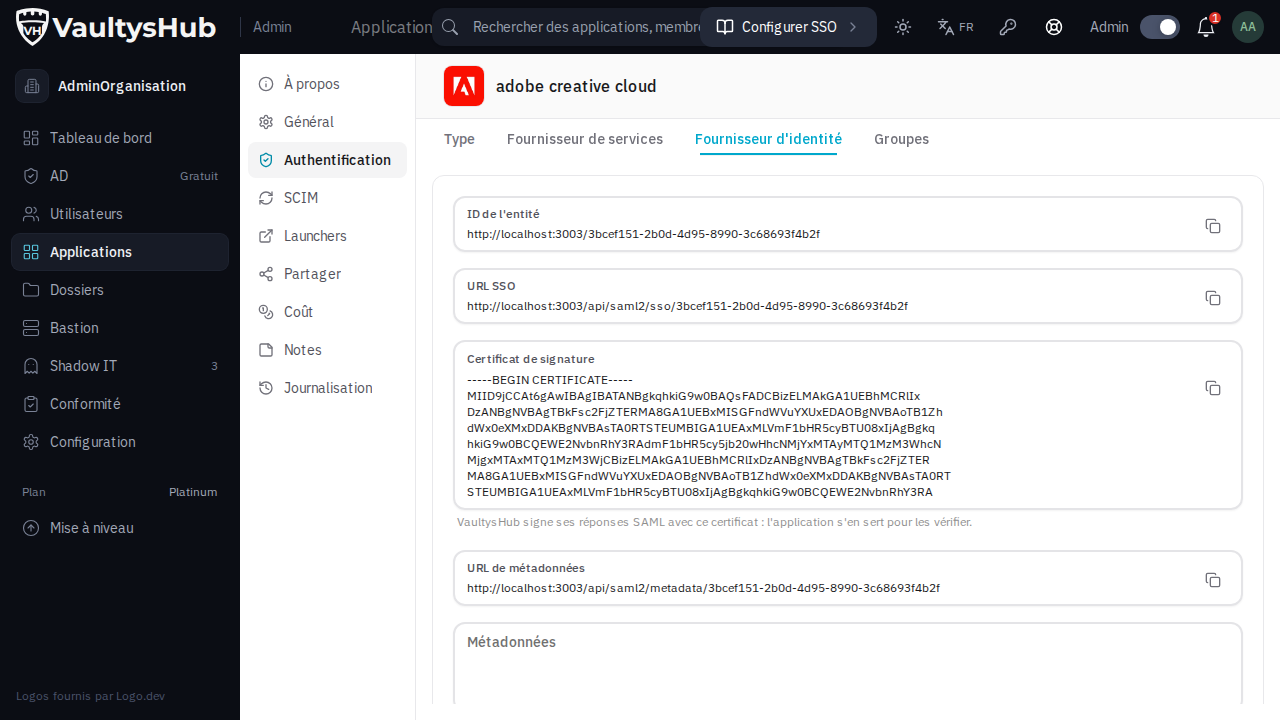
Service Provider Settings
The Service Provider tab contains the information of the external application (SP) to declare in VaultysHub so that it can send SAML assertions to it:
| Parameter | Description |
|---|---|
| Entity ID | Unique identifier of the external application (Service Provider) |
| ACS URL | URL of the external application that receives SAML assertions (Assertion Consumer Service) |
| SLO URL | Logout URL of the external application (Single Logout Service) |
| Certificate | Public certificate of the Service Provider to verify its signed requests |
| Private Key | Private key of VaultysHub to sign assertions sent to the Service Provider |
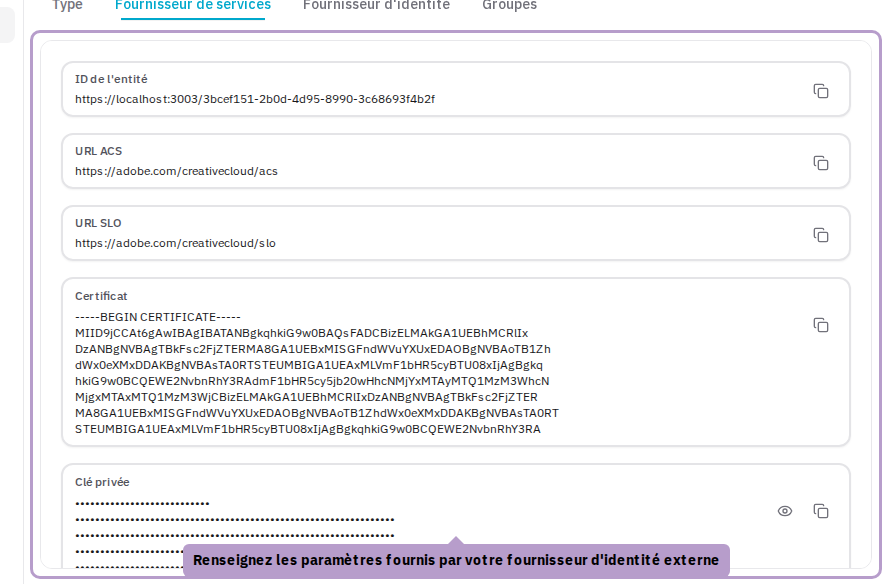
Identity Provider Settings
The Identity Provider tab exposes the endpoints of VaultysHub (IdP) to be filled in your external application:
| Parameter | Description |
|---|---|
| Entity ID | Unique identifier of VaultysHub as an identity provider |
| SSO URL | SSO endpoint of VaultysHub where the application redirects the user |
| Metadata URL | URL of the XML metadata file of VaultysHub (automatic import possible) |
| Metadata | Raw content of the metadata file |
Advanced options allow adjusting the behavior of the signature and the protocol:
| Option | Description |
|---|---|
| Sign assertions | VaultysHub signs the SAML assertions sent to the Service Provider |
| Sign requests | VaultysHub also signs the entire SAML response (the message), in addition to the assertion. The response is signed anyway if the assertions are not. |
| Use HTTP | Allows HTTP connections (not recommended in production) |
OIDC Configuration
Select OIDC from the dropdown menu to enable the OpenID Connect protocol.
Provider Settings
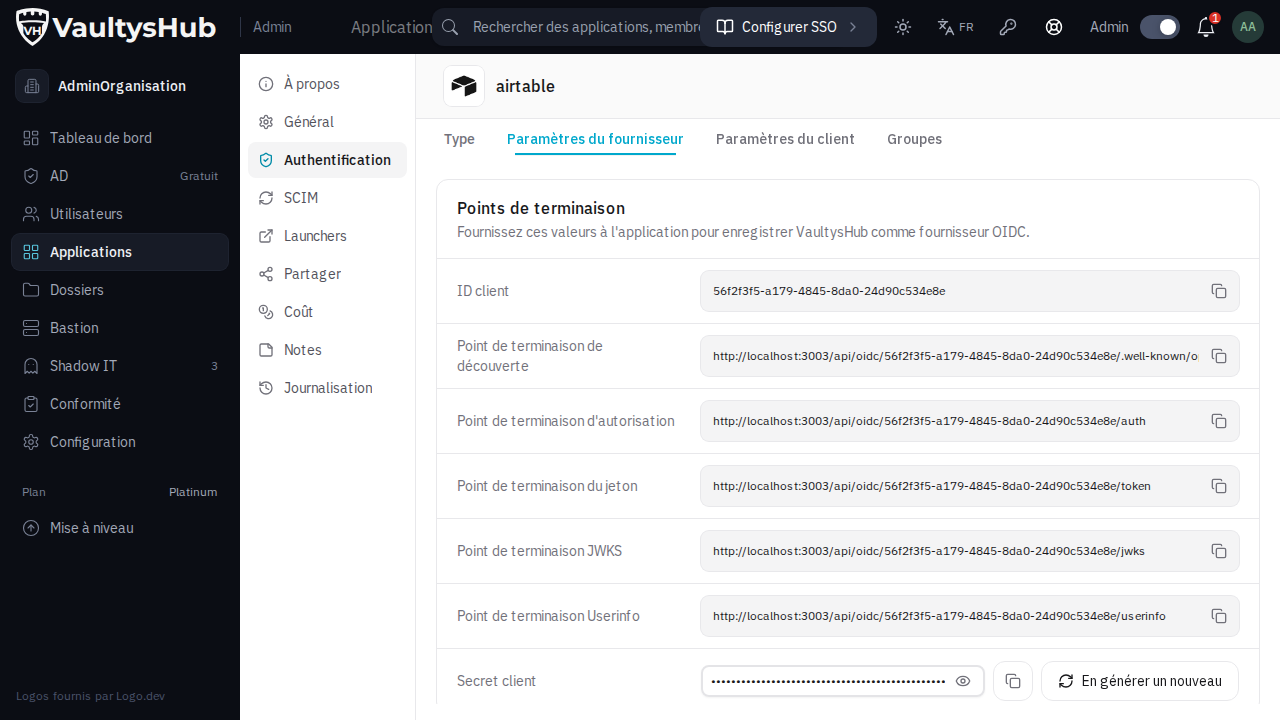
The Provider Settings tab exposes the OIDC endpoints automatically generated by VaultysHub:
| Endpoint | Description |
|---|---|
| Discovery Endpoint | Automatic discovery URL for OIDC configuration |
| Authorization Endpoint | OAuth2 authorization URL |
| Token Endpoint | URL to exchange the authorization code for a token |
| JWKS Endpoint | URL of the public keys for signing tokens |
| Userinfo Endpoint | URL to retrieve user information |
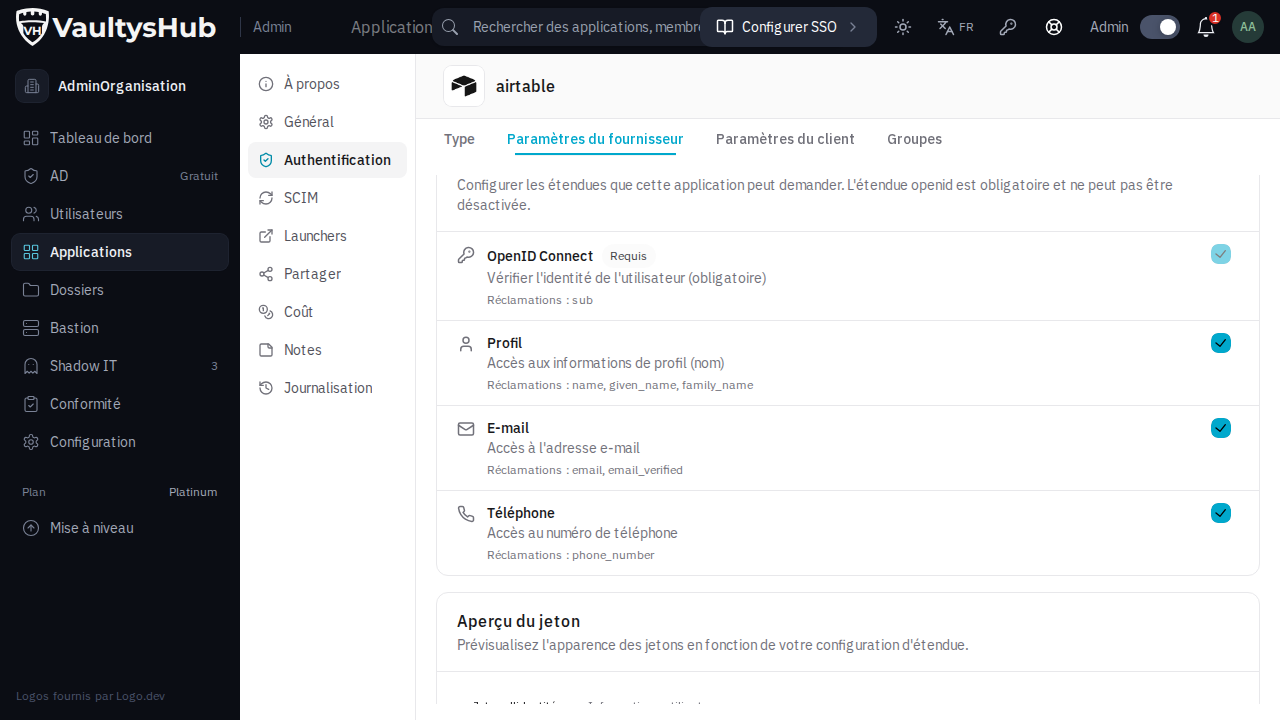
It also allows configuring:
- Client Secret: shared secret between VaultysHub and your client application
- PKCE: strengthening the security of the authorization code flow (recommended)
- Subject Identifier: field used as a unique identifier for the user in the tokens (
membershipIdor email address) - Allowed Scopes: scope of accessible data (
openid,profile,email,phone) - Redirect URIs: allowed URLs for redirection after authentication
Client Configuration
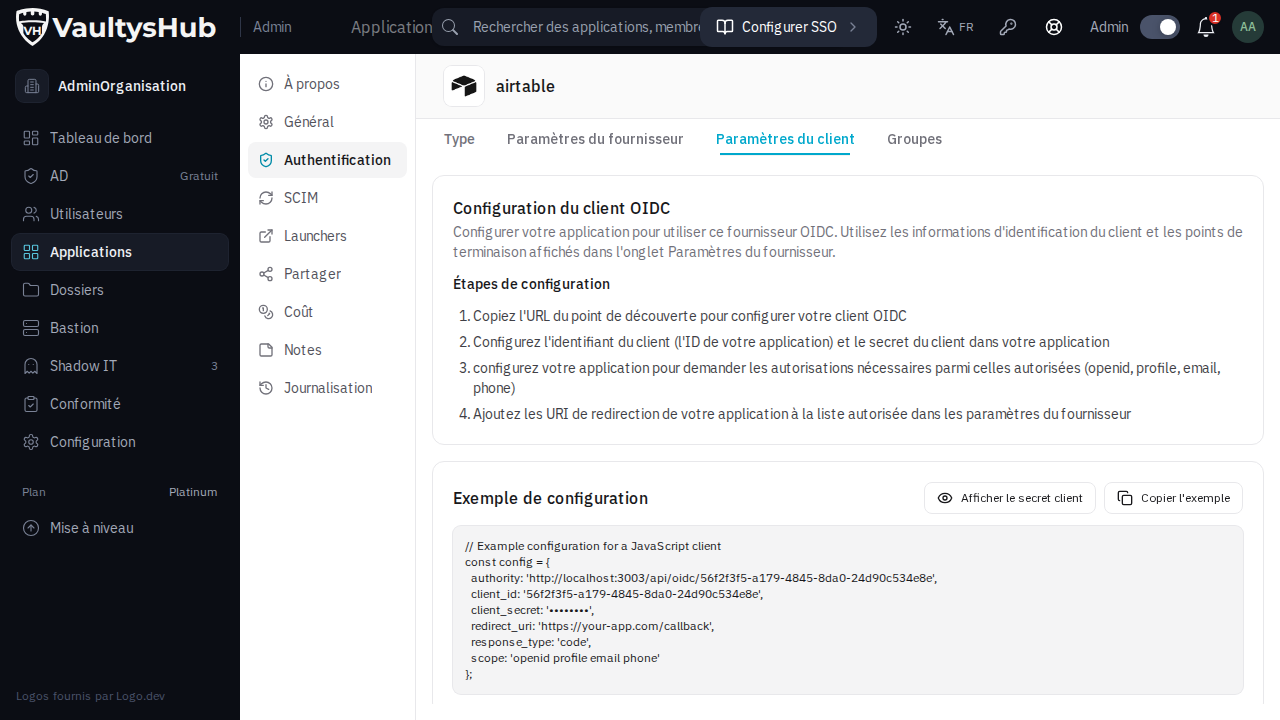
The Client Settings tab provides a ready-to-use code example to integrate VaultysHub as an OIDC provider in your application.
Transmitting User Groups
In OIDC as in SAML, VaultysHub can send the list of groups of the user to the application at each login, so that it can place them immediately in the correct groups or roles. These groups are defined by a mapping between your VaultysHub folders and the group names of the application, in the Groups section of the Authentication tab. They are transmitted in the groups claim of the ID token and the userinfo response in OIDC (the application must request the groups scope, and Send Groups must be checked), or in a multi-valued groups attribute of the assertion in SAML; the name of the claim or attribute is modifiable. See Groups for detailed configuration and examples.
Integration Guides
Step-by-step guides are available to configure SSO with more than twenty common applications (GitLab, Nextcloud, Grafana, Odoo, GLPI, Lucca, Proxmox…). You can find them all on the SSO Integrations page.